bgunderlay bgunderlay bgunderlay
123

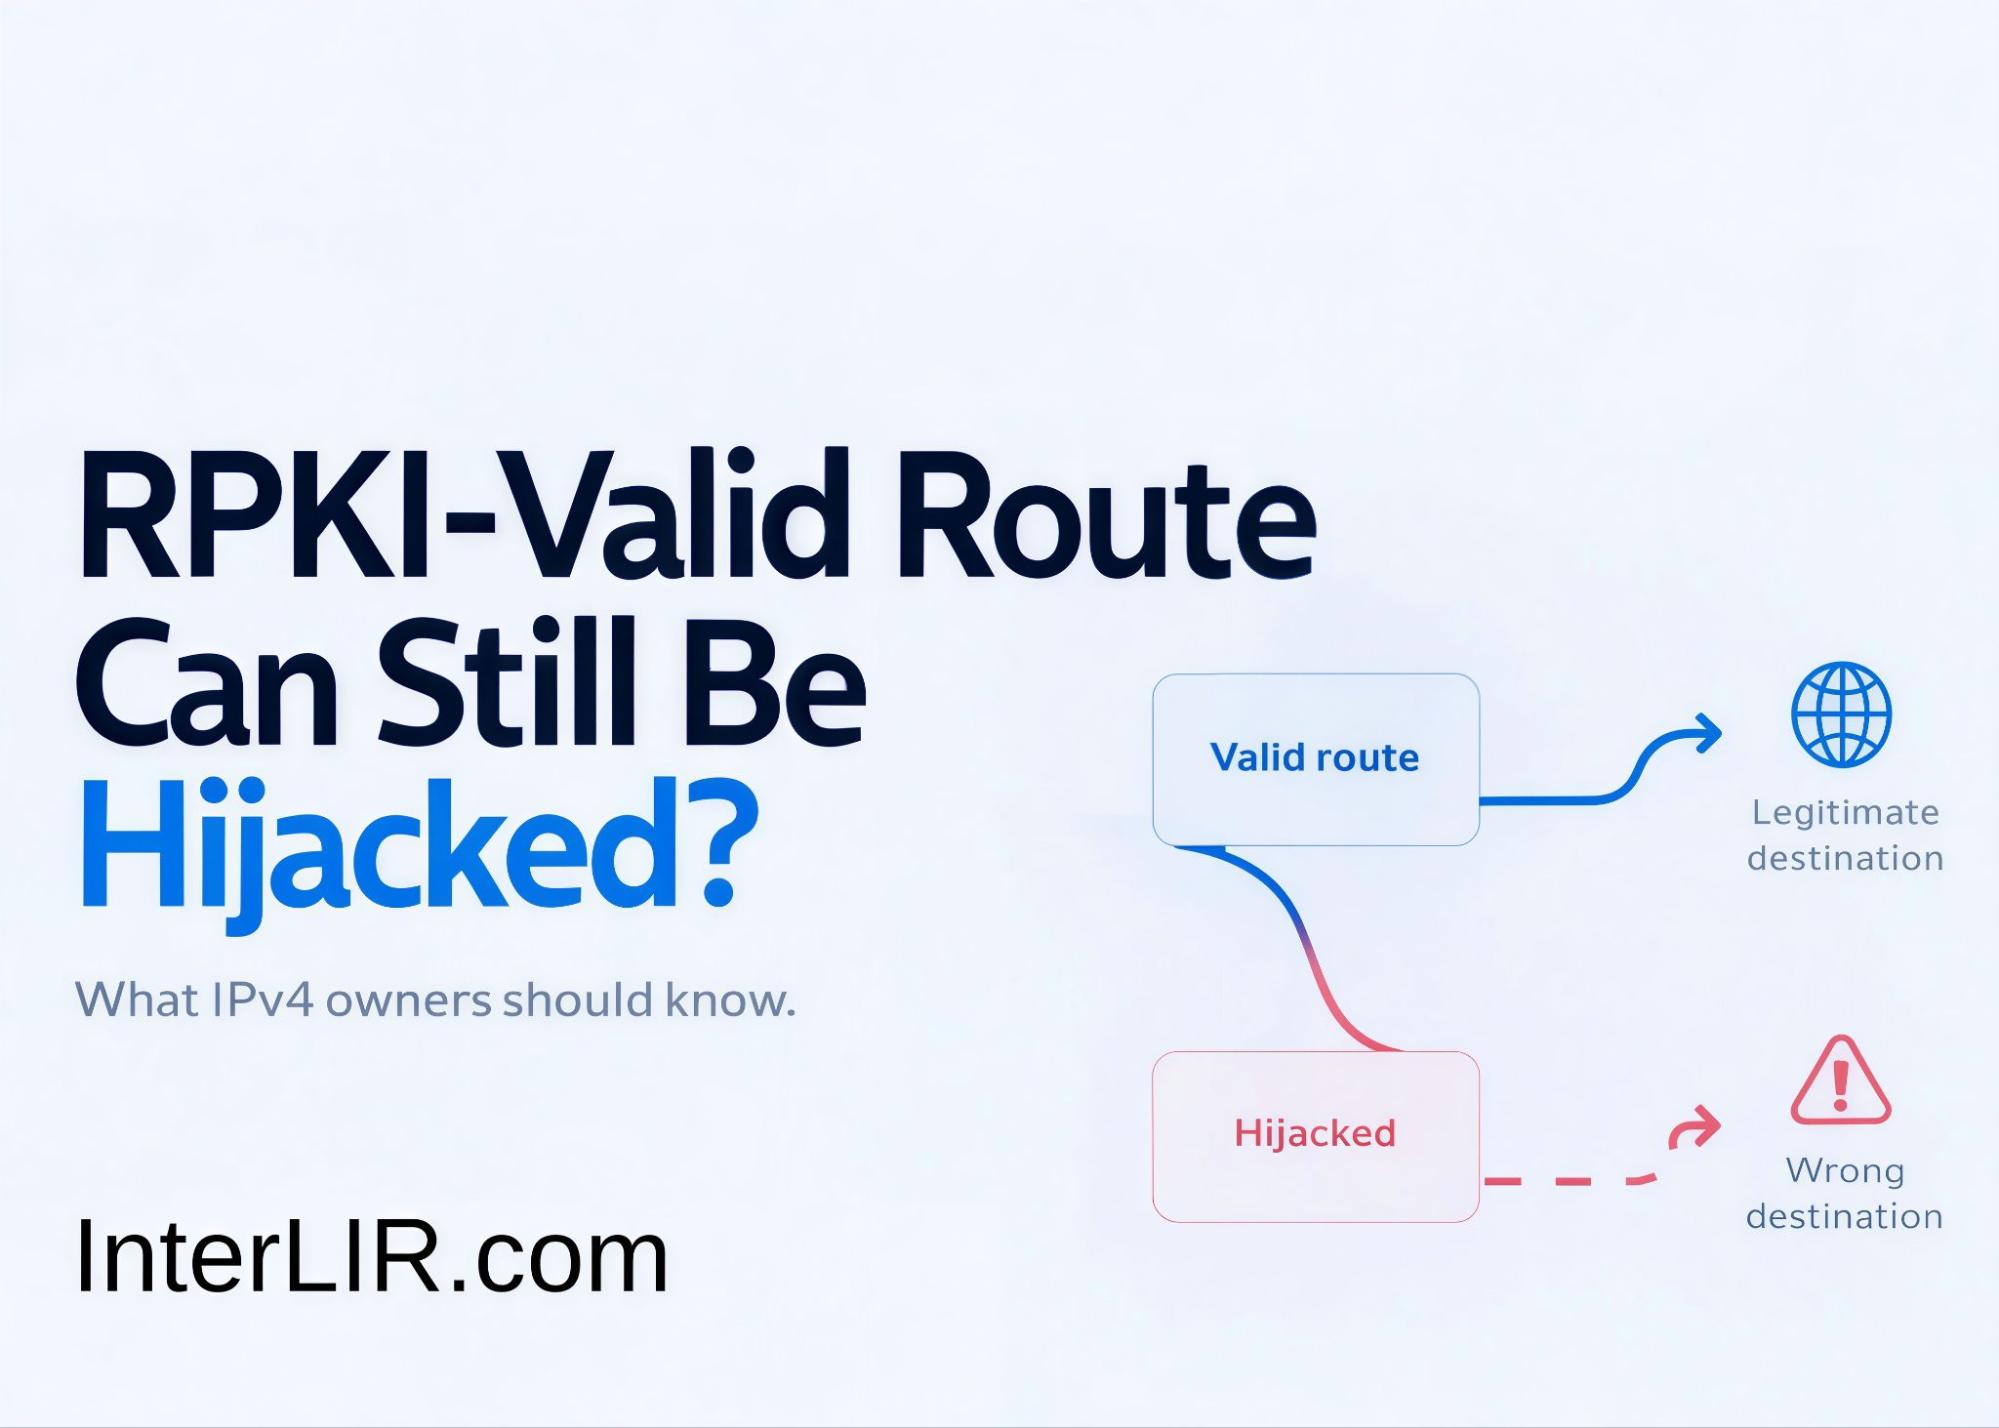
Can an RPKI-Valid Route Still Be Hijacked? What IPv4 Owners Should Know

Your IPv4 prefix has a valid ROA. Your monitoring dashboard shows RPKI: Valid. Does that mean the route is safe? Not necessarily.

In August 2026, infrastructure used by Softaculous and Virtualizor was affected by a BGP hijack in which a more-specific /24 was announced inside a legitimate /16. Traffic was redirected to attacker-controlled infrastructure during two separate periods between August 28 and 30. The incident also enabled the attacker to obtain valid TLS certificates and contributed to a malicious Virtualizor update reaching a small number of installations. The unusual part was that the malicious route was still considered RPKI-valid.

Key takeaway: RPKI-valid does not automatically mean route-trusted.

For IPv4 owners, lessees and network operators, the incident shows why routing security needs to go beyond checking whether a route simply passes Route Origin Validation.

What Happened During the Softaculous BGP Hijack?

At approximately 20:57 UTC on August 28, 2026, a new BGP announcement appeared for: 162.55.80.0/24 That prefix sits inside the larger: 162.55.0.0/16 normally originated by Hetzner Online through AS24940. The affected /24 contained addresses used by Softaculous infrastructure, including software update systems and client-facing services. Softaculous reported two periods of incorrect routing:

Incident period Start End
First period August 28, ~20:57 UTC August 29, ~08:50 UTC
Second period August 29, ~20:57 UTC August 30, ~06:10 UTC

During these periods, traffic intended for legitimate Softaculous systems could instead be routed toward attacker-controlled infrastructure.

Why Did the /24 Override the Legitimate /16?

The reason is a fundamental rule of IP forwarding: the most-specific matching prefix normally wins. A router that sees both of the following routes will generally prefer the /24 for addresses inside that smaller range:

Route Role What happens
162.55.0.0/16 Legitimate route Covers the larger address range
162.55.80.0/24 More-specific route Preferred for traffic inside the /24

The attacker therefore did not need to replace or hijack the entire /16. A single more-specific /24 could attract traffic for the systems located inside that range. LACNIC’s technical analysis described the event as a more-specific hijack of Hetzner’s normal /16 announcement.

How a More-Specific Prefix Redirects Traffic

Normal routing

162.55.0.0/16 announced by the legitimate network

Traffic follows the /16

Legitimate infrastructure receives the traffic

During the hijack

162.55.80.0/24 appears as a more-specific route

Traffic for 162.55.80.x follows the /24

Traffic can be redirected

Caption: BGP forwarding prefers the more-specific /24 over the /16 for addresses inside that range.

How Could the Route Remain RPKI-Valid?

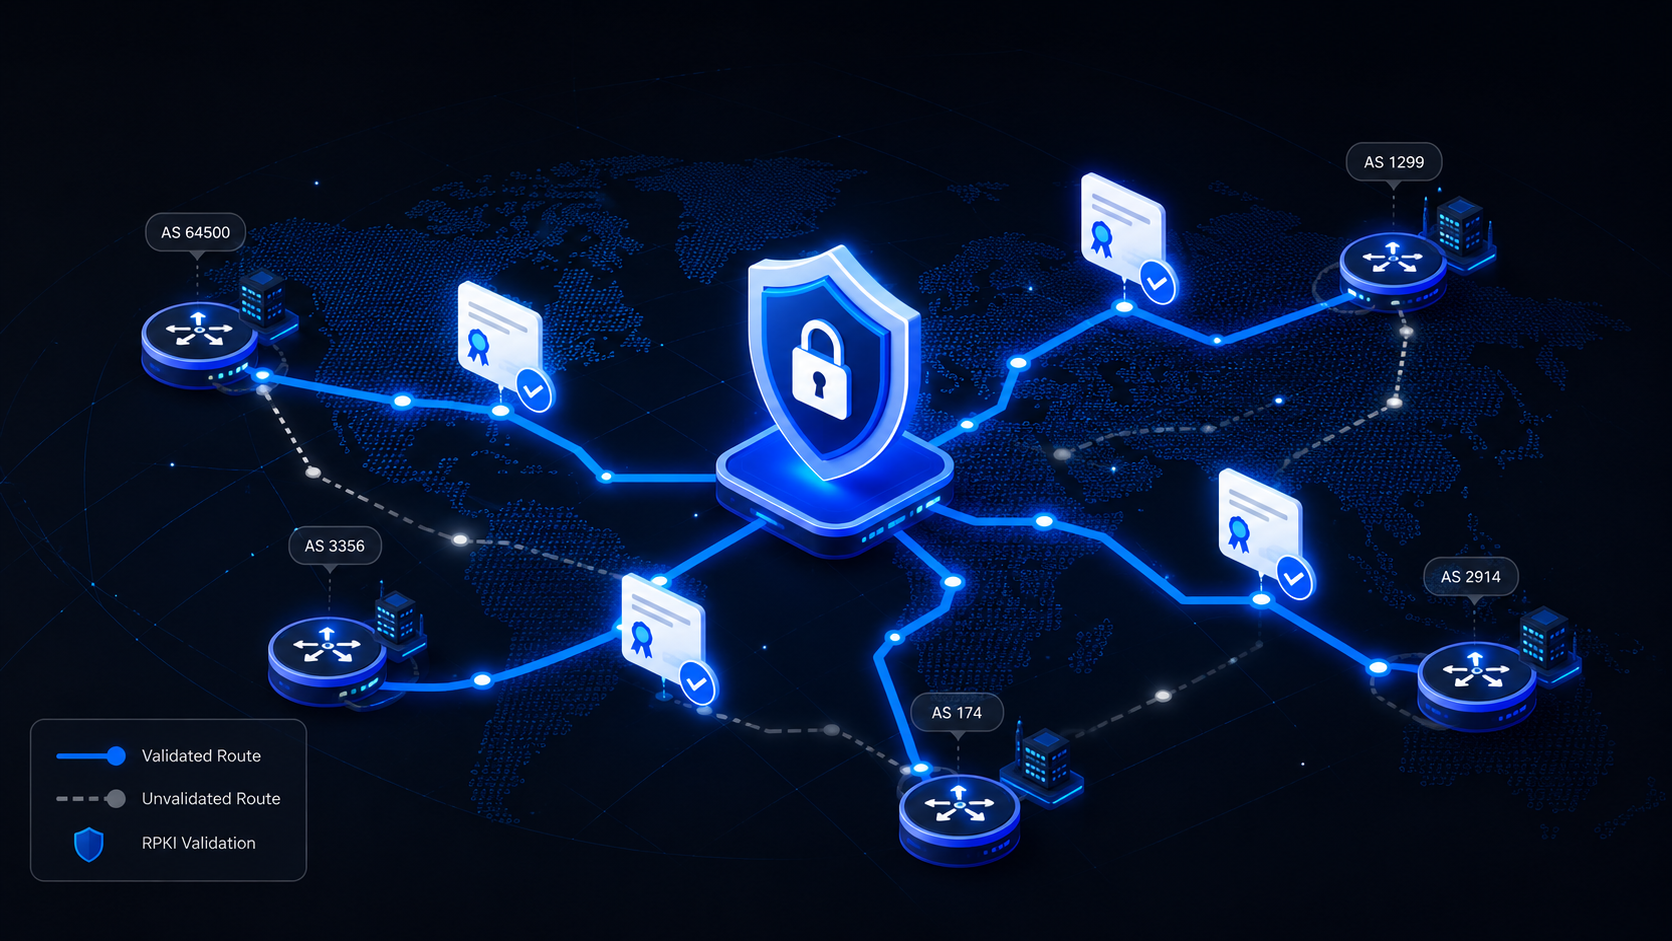
This is the most important part of the incident. The suspicious route was observed with an AS path resembling: … → AS6204 → AS62390 → AS24940 The rightmost ASN — the origin presented by the route — was AS24940, Hetzner’s legitimate ASN. The existing ROA also allowed prefixes within the /16 to be announced as specifically as /24. That meant two important Route Origin Validation checks succeeded:

RPKI check What the route showed Result
Is the origin ASN authorized? Origin appeared as AS24940 ✓ Valid
Is the prefix length authorized? /24 was permitted ✓ Valid
Is the complete AS path legitimate? Standard ROV does not verify this Not checked

The result was therefore:

RPKI status: Valid

The route passed origin validation even though the surrounding BGP path was associated with the hijack.

What Does Route Origin Validation Actually Check?

ROV essentially asks:

Is this ASN authorized to originate this IP prefix?

It does not prove that every autonomous system appearing earlier in the AS path represents a legitimate routing relationship. That distinction matters. An attacker who can make the authorized ASN appear in the origin position may be able to create a route that passes origin validation even though the route itself is malicious.

Why the Hijacked Route Was RPKI-Valid

ROA authorization

Prefix: 162.55.0.0/16

Authorized origin: AS24940

More-specifics allowed to /24

—

Hijacked announcement

Prefix: 162.55.80.0/24

Apparent origin: AS24940

Prefix length: /24

Path included unexpected ASes before the origin

Validation result
✓ Origin ASN matched
✓ Prefix length matched ✓ RPKI VALID
But:
 the complete AS path was not validated by ordinary ROV.

Should you set maxLength in your ROA?

The incident also shows why ROA configuration matters. A ROA can authorize a larger prefix while using maxLength to permit more-specific announcements. For example:

Configuration Prefix Origin ASN maxLength
Broader authorization 203.0.0.0/16 AS64500 /24
Exact authorization 203.0.0.0/16 AS64500 /16

With the first configuration, the ASN can originate more-specific prefixes down to /24 and have them pass Route Origin Validation. That may be operationally useful when the network actually advertises those more-specific routes. But if those prefixes are never used, the authorization can be broader than necessary.

RFC 9319 recommends using minimal ROAs whenever possible and generally avoiding maxLength unless there is a specific operational need. The objective is to reduce the attack surface for forged-origin sub-prefix hijacks.

Following the Softaculous incident, Hetzner changed the ROA for 162.55.0.0/16 so that its maxLength became /16, removing the previous authorization for more-specific prefixes under that ROA.

A practical question for IPv4 owners

Does your ROA authorize more-specific prefixes that your network never actually announces?

If the answer is yes, your authorization may be broader than your current routing requirements.

Not sure your ROA matches what your network actually announces? Send us the prefix and ASN and we’ll compare the ROA, live announcement and IRR objects.

Support chat

How a BGP hijack leads to valid TLS certificates

The routing hijack was only the first stage. Softaculous reported that attacker-controlled infrastructure was able to obtain new TLS certificates for affected domains because certificate-validation traffic was also routed through the hijacked network path. The incident then affected Virtualizor’s update infrastructure. Softaculous confirmed that a malicious update reached a small number of Virtualizor installations. The sequence can be summarized like this:

Stage What happened
1. More-specific BGP route appears A /24 is announced inside the legitimate /16
2. Traffic is redirected Traffic for the affected range follows the /24
3. Certificate validation is affected Validation requests also follow the hijacked route
4. Valid TLS certificates are obtained The attacker can present trusted-looking HTTPS
5. Users and systems connect Connections may not trigger obvious certificate warnings
6. Software delivery is affected A malicious Virtualizor update reaches some installations

This shows why BGP security is not limited to routers. Internet routing sits beneath services such as:

  • TLS certificate validation;
  • software repositories;
  • APIs;
  • DNS infrastructure;
  • authentication endpoints;
  • customer portals;
  • payment and billing systems.

A routing compromise can therefore become the first step in a much broader infrastructure attack.

ASPA vs ROA: what’s the difference?

This is where ASPA — Autonomous System Provider Authorization — becomes relevant. ROA and ASPA address different parts of routing security.

ROA ASPA
Main purpose Validate route origin authorization Validate provider relationships
Connects IP prefix → authorized ASN Customer ASN → authorized providers
Main question Which ASN may originate the prefix? Which providers is the ASN authorized to use?
Helps identify Unauthorized origins Unexpected provider relationships
Deployment Established Still developing

After the incident, Hetzner also added an ASPA record identifying authorized providers for AS24940. According to the technical analysis, networks performing ASPA validation could use that information to reject paths containing an unauthorized upstream relationship such as the one observed in this event. ASPA does not replace ROAs. The mechanisms protect different parts of routing information.

ROA vs ASPA

Security layer — Question it helps answer

ROA

Is this ASN allowed to originate this prefix?

ROV

Does the current BGP origin match the ROA?

ASPA

Is this provider relationship authorized?

BGP monitoring

Has the prefix, origin or AS path changed unexpectedly?

A stronger routing-security model combines these signals rather than relying on only one of them.

What to check before announcing a leased IPv4 block

Before a newly leased IPv4 block is announced, the routing state should be checked against how the block will actually be used.

What to check What to verify before announcement Why it matters
Routing history Previous origins, more-specific announcements and unusual route changes Establishes whether the block has had unexpected routing activity
Authorized origin ASN The ASN that should originate the block in the new setup Prevents a mismatch between the intended origin and the ROA
ROA configuration Authorized ASN and permitted prefix length Ensures the ROA matches the actual announcement plan
IRR route objects Existing route objects and the ASN they reference Avoids stale routing records after operational control changes
Expected announcement size Whether the block will be announced as the full prefix or as approved more-specifics Helps avoid unnecessarily broad maxLength authorization
AS-path baseline Expected upstreams and normal path structure Makes unexpected provider or path changes easier to detect
Reputation and abuse history Current blocklist status and recent abuse history Identifies non-routing risks before production use
Geolocation Whether major geolocation databases reflect the intended region Reduces regional access and service issues after deployment

If the block moves to a different ASN, transit provider, cloud environment or BYOIP setup, update the relevant routing authorization and route objects before announcing it.

Registry ownership or lease status can remain correct while the routing configuration is still outdated. The operational check should therefore be performed against the planned live announcement, not only against registry data.

RPKI-Valid Does Not Mean Route-Trusted

The Softaculous incident demonstrated an important limitation of Route Origin Validation: the malicious /24 could satisfy the ROA because the apparent origin matched the authorized ASN and the ROA permitted that prefix length.

RPKI remains an important routing-security layer, but it answers a specific question about origin authorization. It does not validate the complete AS path. For IPv4 owners, lessees and operators, the practical conclusion is to keep ROAs precise and combine origin validation with route and path monitoring.

Do not stop your routing-security checks when a route says “RPKI Valid.”

Browse available IPv4 blocks by RIR and region on the InterLIR Marketplace.
Browse IPv4 Marketplace

Sources

Why IP Geolocation Can Be Wrong After an IPv4 Transfer

An IPv4 transfer changes registry data, but GeoIP providers may continue to show the old country. Learn which records matter and how to request corrections.

IP geolocation after an IPv4 transfer does not update everywhere at the same time. The Regional Internet Registry may show the new resource holder while a website, advertising platform or streaming service still assigns the block to its previous country. This can happen because registry records, routing data, operator-published geofeeds and commercial GeoIP databases are separate systems.

To correct an outdated location, the recipient should verify the RIR record, publish an accurate geofeed, check the live BGP announcement and submit evidence to the databases used by affected services. No single change can force every provider to update, and no broker can guarantee one universal correction date.

Why IP Geolocation After an IPv4 Transfer Can Be Wrong

An IPv4 address transfer changes the registration of an eligible prefix from a source organisation to a recipient organisation. It does not automatically rewrite every third-party database that has previously associated the prefix with a country, city, company or connection type.

GeoIP providers build their own datasets from multiple signals. These may include operator submissions, registry records, routing observations, network measurements, customer feedback and historical evidence. Providers use different sources, confidence rules and release schedules, so two current databases can return different answers for the same IP address.

A transfer can also be followed by a genuine change in deployment. A block previously used in one region may be deployed in another country or operated by a different network. Until providers obtain and process evidence of that change, historical location data can remain visible. However, a change of registered holder alone does not necessarily mean that the block’s geographic location has changed.

Why Does WHOIS Show the Right Country but the Website Still Shows the Wrong One?

RIR databases primarily document Internet number-resource registration and contacts. A country: value may describe an administrative or registration context rather than the physical location of every device using the prefix. It is therefore useful evidence, but it should not be treated as a definitive GeoIP record.

RFC 9632 explicitly distinguishes operator-published geofeed data from geographic hints in RIR objects. Under its discovery rules, consumers must disregard other geographic hints for the relevant address range, such as country: or geoloc:, when a geofeed is specified. This does not guarantee that every commercial provider will accept the declared location without its own checks.

The distinction matters for multinational networks, cloud infrastructure, leased address space and anycast services. The registered organisation may be in one country while users or infrastructure are distributed across several others.

Which Data Source Is My Service Actually Using: RIR, Geofeed or a GeoIP Vendor?

Source What it can show Updated by the transfer? How to correct it
RIR RDAP/WHOIS Registered holder, contacts, status and registry country data The holder record is updated through the RIR process Use the relevant RIR or sponsoring LIR procedure
Geofeed Operator-declared country, region and city by prefix Not automatically Publish an RFC 8805 geofeed and reference it through the registry’s supported mechanism
BGP Observed announcements, prefixes and origin ASNs No; routing must be reviewed separately Coordinate any required announcement changes, IRR objects and RPKI ROAs
Commercial GeoIP Vendor estimate of user or network location Not necessarily; providers process evidence independently Provide consistent evidence through each vendor’s correction channel
Online service The service’s own interpretation, API result or licensed database snapshot Not automatically Identify its data supplier or use the service’s reporting process
From transfer records to the location shown by an online service
1. RIR record
Holder and administrative data
REGISTRATION UPDATE
2. Geofeed
Operator-declared deployment location
OPERATOR-MAINTAINED
3. BGP / RPKI
Live origin and route authorisation
SEPARATE VERIFICATION
4. GeoIP vendor
Independent estimate and release cycle
INDEPENDENT PROCESSING
5. End service
Vendor feed, local database or cached API result
SERVICE-SPECIFIC UPDATES

The arrows show a practical review workflow, not automatic synchronisation or a mandatory data path. Registry, geofeed and routing checks can run in parallel. GeoIP vendors choose their own evidence sources, and online services control how they use and refresh the resulting data.

Step 1: Verify the Transfer and Registry Record

Start with the authoritative registration data for the prefix. Confirm that the transfer is complete, the recipient organisation is displayed correctly and the abuse and administrative contacts are current. If the block is subdivided for customers, make sure any permitted more-specific assignments or suballocations are also accurate.

Do not change a registry country field solely to influence a consumer website. The record should accurately reflect the purpose defined by the relevant RIR. An inconsistent or misleading registry object can make correction requests less credible rather than more effective.

Step 2: How to Create a Geofeed File (RFC 8805 Example)

RFC 8805 defines a CSV format for publishing IP location data: ip_prefix,alpha2code,region,city,postal_code. Use ISO 3166-1 alpha-2 country codes and ISO 3166-2 region codes. Only the prefix is required; leave unknown location fields empty. The postal-code field is deprecated and should remain empty.

Choose prefixes that accurately represent deployment. If parts of a /20 serve different countries, publish more-specific entries for those parts. There is no need to split a block further when the same location accurately applies throughout it.

Host the file at a stable HTTPS URL. Use the relevant registry’s supported mechanism to reference it. For RPSL objects, RFC 9632 prefers geofeed: where supported and also defines the remarks: Geofeed form.

RFC 9877 defines how geofeed links can be exposed through RDAP. Follow the relevant RIR’s procedure; do not assume that every registry offers the same field or interface.

Example geofeed entries

192.0.2.0/24,DE,DE-BE,Berlin,
198.51.100.0/25,ES,ES-M,Madrid,
198.51.100.128/25,ES,ES-B,Barcelona,

These are documentation prefixes; replace them with authorised networks and verified locations. Save the actual CSV as UTF-8 with CRLF line endings and one record per line, without a header row. The trailing commas preserve the empty postal-code field. The /25 entries describe location granularity, not a requirement to announce /25 routes separately in BGP.

Step 3: Do BGP and RPKI Affect IP Geolocation?

A correct geofeed can still conflict with the network’s live operation. Verify that the observed announcements match the agreed deployment and that the authorised origin ASN is visible. This may be the recipient’s ASN or an ASN operated by its hosting, transit or other authorised network provider. A transfer does not, by itself, require a change of origin ASN.

Coordinate the withdrawal of obsolete or unauthorised announcements where necessary. Confirm that the appropriate RPKI Route Origin Authorisations (ROAs) cover the intended origin ASN and announced prefix lengths, maintain accurate IRR route objects, and review reverse DNS and abuse contacts.

BGP does not prove a user’s physical country, and a ROA authorises route origination rather than geographic location. An ASN can operate globally, and traffic can traverse remote upstreams or Internet exchanges. An unchanged origin ASN or multiple origin ASNs are not automatically errors; investigate whether the announcements are authorised and consistent with the deployment described in the correction request.

RPKI updates pass through repository publication, validator refresh and router-cache synchronisation. RFC 8210 specifies a recommended default of 3,600 seconds (one hour) for a router to poll its RPKI cache; a cache notification can prompt an earlier query. This is not an end-to-end propagation deadline. Check the ROA’s publication and the observed validation state rather than assuming that every network will reflect the change within one or two hours. If a route is invalid, check the authorised ASN and prefix length as well as possible stale data.

An IRR change also has several stages: acceptance by the authoritative registry, replication to any mirrors, and use by an upstream provider’s route-filtering system. Their schedules differ. Confirm the object in the authoritative IRR, then check which database and filter-refresh process the transit provider actually uses.

Step 4: Submit Corrections to GeoIP Providers

Once you have verified the public records and deployment, check several databases using addresses from each deployed subprefix. Record the returned country, region, city, organisation and connection type where available. Prioritise providers that are known to supply the affected product; correcting an unrelated lookup site may have no impact.

MaxMind provides an official GeoIP location correction form for an IP or network. It reviews requests against multiple data sources and does not guarantee acceptance. IPinfo also maintains an IP geolocation correction channel. Submit the exact CIDR, verified deployment location, company-domain contact and supporting geofeed or registry links, following each provider’s requirements.

If Google products show the wrong country, use Google’s IP problem reporting process. Google states that updates may take more than a month and that it does not provide an individual follow-up. A submitted request is therefore not an immediate correction.

Step 5: How to Check If the Geolocation Fix Worked

A public GeoIP demo does not necessarily use the same database version, product tier or custom rules as the service experiencing the problem. Test the actual search engine, payment gateway, advertising platform, content service or customer application affected by the error.

Use several addresses from the prefix and repeat tests from fresh sessions where appropriate. Confirm which public IP the service actually sees, especially when a VPN, proxy or NAT gateway is involved. Some services also consider account settings, device location and previous activity, so an unexpected country is not always caused by their GeoIP database.

Keep dated screenshots or API responses, the exact tested IPs and correction-ticket references. This creates a usable escalation record and helps distinguish an outdated vendor database from a cached application result or another location signal.

How Long Does a GeoIP Correction Take?

There is no universal update period. A provider must first receive or discover the new evidence, validate it and include any accepted correction in its data. Its customer must then download a new database release or obtain a refreshed API result. A downstream platform may apply additional rules or retain older data.

Routing and registry checks support an orderly transfer, but their completion does not set the timetable for a GeoIP correction.

Layer When the change becomes visible What can delay it
RPKI ROA After publication, validator processing and router-cache synchronisation; no universal end-to-end deadline Repository errors, failed validation, refresh intervals or stale caches
IRR route object After registry acceptance; mirrors and upstream filters update separately Authentication review, replication schedules or upstream provisioning
GeoIP provider correction After review and publication; Google warns that its updates may take more than one month Conflicting evidence, review requirements or release schedules
API-client cache When the application refreshes its stored result; there is no standard cache lifetime Custom TTL, additional cache layers or results stored without automatic refresh
Downloaded GeoIP database When the customer downloads and deploys a build containing the correction Update schedules, failed downloads or delayed deployment

Allow for provider-specific review and downstream update delays rather than assuming that the country will change when the RIR approves the transfer. Some services may take weeks or longer. Monitor progress by provider and avoid promising customers a single completion date.

A vendor API and a downloaded database behave differently. An API may expose corrected data once it is available in that product, but the customer application may retain its previous answer according to its cache policy. A local database remains unchanged until the customer downloads and deploys another build.

MaxMind’s database-update guidance recommends automation and checking periodically throughout the day for releases, including off-schedule updates. Its sample twice-weekly cron schedule is an example of customer-side download automation, not a correction deadline. If the vendor’s own lookup is correct but the end service is still wrong, check the database product, build date, cache policy and other location signals used by that service.

Not Sure Your Geofeed, Routing and Registry Data Agree?

Send us the prefix and we’ll check the public RIR record, geofeed, BGP origin, RPKI status and the main GeoIP databases for conflicting signals.

Check My IP Block

Common Reasons a Correction Fails

  • the transfer is complete, but an obsolete more-specific record still identifies the previous organisation;
  • the geofeed is unreachable, malformed or not discoverable through the registry or the provider’s submission process;
  • one geofeed row assigns a mixed-location block to a single country;
  • the observed announcements conflict with the deployment described in the request;
  • the requested country reflects the company’s registered address rather than the actual deployment;
  • only one GeoIP vendor was contacted while the affected service uses another source;
  • the provider has corrected its data, but the downstream service still uses an older database or cached result;
  • the service’s displayed country is influenced by account or device settings rather than IP geolocation alone.

GeoIP Checklist Before and After an IPv4 Transfer

Before the transfer

  • check representative addresses across the full prefix and relevant more-specifics in several GeoIP databases;
  • record current RIR, BGP, RPKI, IRR and geofeed data;
  • define the intended deployment locations and the prefixes to which they apply;
  • agree on technical cooperation, authorised origin ASNs and any required announcement withdrawals or changes;
  • review IP reputation as a separate risk; accurate geolocation does not establish that a block is free of abuse history or suitable for a particular service.

After the transfer

  • verify the recipient and contacts in RIR records;
  • publish or update an accurate geofeed and reference it using the registry’s supported mechanism;
  • verify BGP, RPKI, IRR and reverse-DNS records and complete any required changes;
  • submit GeoIP corrections with consistent evidence where location data is outdated;
  • test the affected customer-facing services and track unresolved discrepancies by provider.

Organisations planning to buy IPv4 address space should include geolocation verification in the transfer plan. Document the actual deployment, the services that need to recognise it correctly and the acceptable lead time before deployment.

Need IPv4 Space for a Specific Region?

Browse available IPv4 blocks on the InterLIR marketplace and find options for your next acquisition.

Browse IPv4 Marketplace

Sources and Further Reading

Why Does an IP Address Show the Wrong Country? IP Geolocation Explained

IP geolocation is an estimate, not a physical property inside an IP address. When an IP address shows the wrong country, the problem is usually caused by outdated databases, old usage history, routing changes, missing geofeed data or inconsistent provider records.

For companies leasing, buying or moving IPv4 resources, wrong IP geolocation can create customer complaints, access blocks, fraud checks, regional content errors and support costs.

Businesses often ask the same question after deploying a new IPv4 block: why does this IP address show the wrong country? The routing may be technically correct, the server may be online and the documentation may be valid, but websites and applications may still identify the address as being located somewhere else.

The reason is simple: IP geolocation providers do not read a built-in country field from the IP address. They estimate location using multiple data sources. Those sources can be outdated, incomplete or interpreted differently by each provider.

Quick answer: an IP address can show the wrong country because IP geolocation databases are based on estimates from registry data, routing signals, geofeeds, historical usage, network measurements and correction requests. If those signals lag behind a lease, transfer or routing change, different services may show different locations.

Key takeaways about IP geolocation

1

IP addresses do not contain location

IP geolocation is inferred from external sources, not encoded inside the address.

2

Databases update at different speeds

One platform may show the correct country while another still uses older IP geolocation data.

3

Geofeeds reduce guesswork

A geofeed gives providers a structured prefix-to-location source for IP geolocation.

4

Wrong location has business impact

Incorrect IP geolocation can trigger access blocks, fraud alerts and regional service errors.

What is IP geolocation?

IP geolocation is the process of estimating the geographic location of an IP address. The estimate may include country, region, city or network-level information, depending on the database and use case.

An IP address itself does not contain a country, city or street address. There is no field in an IPv4 or IPv6 address that says where the user, server or company is physically located. IP geolocation companies build location estimates from signals such as RIR records, WHOIS and RDAP data, BGP routing, traceroutes, ISP information, historical use, geofeeds and user-submitted corrections.

This is why IP geolocation is not exact science. It is a data pipeline. When the inputs are stale or inconsistent, the output can be wrong.

Why an IP address shows the wrong country

Cause What happens Typical fix
Outdated IP geolocation database The database still reflects the old country or previous network. Submit corrections and publish accurate geofeed data.
Previous use in another country Old history follows the IPv4 block after lease, transfer or reassignment. Audit locations before deployment and request updates early.
Different provider methodologies One website shows Germany, another shows the Netherlands, another shows France. Check multiple vendors and correct the highest-impact databases.
Missing geofeed Providers rely on indirect signals because no structured operator data is available. Publish a valid geofeed and reference it where supported.

IP geolocation source 1: outdated databases

The most common reason an IP address shows the wrong country is simple delay. IP geolocation providers update their databases on different schedules. If an IPv4 block was recently leased, transferred, moved to a new ASN or deployed in another country, some databases may still show the previous location.

This is why different websites can show different results for the same IP address. A fraud prevention tool, search engine, streaming platform and analytics provider may each rely on a different IP geolocation vendor or database version.

IP geolocation source 2: old IPv4 history

IPv4 address blocks often have long histories. A prefix may have been used by one provider in one country for years, then leased or transferred to another organization in another region. The registry data may update quickly, but IP geolocation systems may still associate the prefix with the old location.

This is especially common in the IPv4 secondary market. The commercial control of an IP block may change faster than all external databases, security platforms and content systems can react.

IP geolocation source 3: different data sources

There is no single global IP geolocation authority. Providers use their own methods and datasets. Some place more weight on registry data. Others use routing signals, network measurements, customer submissions, geofeeds or historical patterns.

Because methodologies differ, IP geolocation results can differ. That does not always mean one provider is broken. It often means the available signals point in different directions or were updated at different times.

IP geolocation source 4: network infrastructure location

Sometimes the business location and infrastructure location are not the same. A company may be registered in one country, lease IPv4 addresses from a marketplace, announce the prefix through a different ASN and host servers in a data center in another country.

Some IP geolocation systems may classify the address based on the network infrastructure location. Others may infer location from the resource holder, registry information or user traffic patterns. The result can look inconsistent to customers.

IP geolocation source 5: missing or incorrect geofeed data

A geofeed is a CSV file that maps IP prefixes to geographic information such as country, region and city. RFC 8805 describes the self-published geofeed format and explains that network operators can publish prefix-to-location mappings for interested parties to consume.

Without a geofeed, IP geolocation providers may rely on less direct signals. With a correct geofeed, the operator gives providers a machine-readable source that can reduce guesswork. A geofeed does not guarantee instant correction everywhere, but it makes corrections more scalable and consistent.

Example geofeed entry

203.0.113.0/24,DE,DE-BE,Berlin,

The example means that the prefix should be associated with Germany, the Berlin region and the city of Berlin. The exact data should match operational reality and should not expose overly precise information about individual users.

IP geolocation source 6: routing and ASN changes

BGP routing changes can influence IP geolocation. When a prefix moves to a new origin ASN, a new upstream provider or a new geography, some systems may temporarily infer a different location. These changes are common during migrations, new IPv4 leases, provider changes and regional expansions.

Routing stability helps IP geolocation providers build confidence in location data. Frequent origin changes, inconsistent route objects or missing RPKI/ROA records can make the onboarding process harder.

Why wrong IP geolocation matters

Wrong IP geolocation is not just a cosmetic issue. It can affect customer access, platform trust and revenue. A user may be asked for extra verification because a login appears to come from a different country. A streaming or content service may apply the wrong region. An ad platform may misclassify traffic. A compliance-sensitive service may apply the wrong rules.

Access problems

Customers may be blocked, challenged or routed to the wrong regional service.

Fraud checks

Legitimate sessions may look suspicious because the IP location does not match user context.

Support workload

Support teams may receive complaints that are hard to diagnose without geolocation checks.

Business reporting

Analytics, advertising and compliance systems may classify traffic incorrectly.

How to improve IP geolocation accuracy

No company can force every IP geolocation provider to update instantly. But there are practical steps that improve accuracy and reduce confusion.

1. Publish a geofeed

Provide structured prefix-to-location data in the RFC 8805 format and keep it current when prefixes move.

2. Reference geofeed data

RFC 9632 specifies how geofeed data can be discovered through RPSL inetnum objects and optionally authenticated using RPKI.

3. Keep registry records clean

Review WHOIS and RDAP information, abuse contacts and organization details so databases do not rely on stale signals.

4. Stabilize routing

Use consistent BGP announcements, route objects and RPKI/ROA records so location signals are easier to interpret.

5. Contact major providers

Submit corrections to the IP geolocation providers that matter most for your customers and applications.

6. Monitor after deployment

Check several databases during the first days and weeks after a lease, transfer or ASN migration.

IP geolocation checklist for leased or acquired IPv4

When a company leases or acquires IPv4 address space, IP geolocation should be checked before customer traffic starts. The best time to fix wrong-country data is before users notice the problem.

Pre-deployment checklist

  1. Check the prefix across multiple IP geolocation databases.
  2. Record country, region and city mismatches.
  3. Confirm the intended infrastructure location and customer geography.
  4. Publish or update the geofeed before production traffic starts.
  5. Review WHOIS, RDAP, route objects and RPKI/ROA records.
  6. Submit correction requests to high-impact providers.
  7. Monitor changes after routing goes live.

How InterLIR helps with IP geolocation issues

InterLIR helps make IPv4 resources usable, not just available

When businesses lease, buy or transfer IPv4 space, InterLIR helps them think beyond availability and price. Operational readiness includes routing, authorization, reputation and IP geolocation accuracy.

For customer-facing services, correcting wrong-country IP geolocation before production can reduce access issues, support tickets and trust problems.

IP geolocation should be part of the onboarding workflow for any leased or acquired IPv4 block. The earlier the location data is checked, the easier it is to avoid customer-facing disruption.

FAQ about IP geolocation and wrong country results

Why does my IP address show the wrong country?

Your IP address may show the wrong country because IP geolocation databases rely on estimates. The database may still use old location data, previous usage history, outdated routing signals or missing geofeed information.

Does an IP address contain its physical location?

No. An IP address does not contain a built-in physical location. IP geolocation providers infer location from external data sources such as registry records, routing data, geofeeds and correction reports.

Why do different websites show different IP locations?

Different websites may use different IP geolocation vendors or database versions. One provider may update quickly while another provider still shows older location data.

Can a geofeed fix wrong IP geolocation?

A geofeed can improve IP geolocation accuracy by giving providers a structured source of prefix-to-location information. It does not guarantee instant correction across every database because each provider has its own validation and update process.

How long does an IP geolocation correction take?

The timing depends on the IP geolocation provider. Some corrections may appear quickly, while others may take days or weeks depending on the provider’s update cycle, validation process and data sources.

Conclusion: wrong IP geolocation is a data problem

When an IP address shows the wrong country, the address itself is usually not broken. The problem is usually that one or more IP geolocation data sources are outdated, incomplete or inconsistent.

Businesses can improve IP geolocation accuracy by keeping registry information clean, publishing geofeed data, maintaining stable routing, submitting corrections to major providers and monitoring results after IPv4 leasing, transfer or reassignment. For companies that rely on customer-facing infrastructure, this work should be part of normal IPv4 onboarding.

IPv4 Leasing Myths: What Businesses Need to Know in 2026

IPv4 leasing is no longer a temporary workaround for companies that cannot buy address space. In 2026, it is a normal infrastructure option for hosting providers, cloud platforms, ISPs, VPN services, SaaS products, data centers and enterprises that still need reliable IPv4 connectivity.

The real question is not whether leased IPv4 addresses are worse than purchased ones. The real question is whether the IPv4 block is clean, correctly authorized, securely routed, properly documented and actively monitored.

The IPv4 market exists because the free supply of IPv4 addresses has been exhausted for years. RIPE NCC announced in 2019 that it had run out of available IPv4 addresses and could only allocate small amounts of recovered space through a waiting list. IPv6 adoption continues to grow, but many internet services still operate in dual-stack environments where IPv4 and IPv6 coexist.

This is why IPv4 leasing remains important. Businesses need address resources for hosting, cloud infrastructure, customer onboarding, regional expansion, BYOIP projects, email platforms, proxy networks, security services and migration work. Buying IPv4 may be right for some long-term strategies, but IPv4 leasing often gives companies more flexibility and lower upfront cost.

Quick answer: the most common IPv4 leasing myths are that leased addresses are lower quality, only suitable for small companies, unsafe for long-term use or irrelevant because IPv6 will replace IPv4 immediately. In practice, IPv4 leasing quality depends on reputation, routing, RPKI/ROA, documentation, abuse handling, geolocation and provider reliability.

Key takeaways about IPv4 leasing myths

1

Ownership is not quality

A leased IPv4 block can perform well when reputation, routing and documentation are clean.

2

Flexibility has value

IPv4 leasing helps companies scale up, test markets or reduce unused address capacity.

3

IPv6 does not remove IPv4 today

IPv6 is growing, but many customers, networks and platforms still require IPv4 reachability.

4

Provider quality matters

Contracts, support, RPKI, abuse handling and transparency define operational readiness.

Why IPv4 leasing remains relevant in 2026

The internet is moving toward IPv6, but it is not moving at the same pace everywhere. Google publicly measures the percentage of users that access Google over IPv6, which shows that IPv6 deployment is significant but still uneven across regions and networks. That unevenness keeps IPv4 operationally important for many production services.

For businesses, IPv4 leasing solves a practical problem: they need usable IPv4 address space now, but they may not want to buy permanent resources before demand is proven. A company may need a /24 for a regional deployment, several prefixes for customer separation or additional space for a short-term migration. In those cases, IPv4 leasing can be faster and more capital-efficient than a purchase.

The mistake is treating IPv4 leasing as a commodity transaction. A low monthly price is not enough. The provider must be able to support clean authorization, correct routing, stable registry information, abuse response and reputation monitoring.

IPv4 leasing myth map: what businesses often get wrong

IPv4 leasing myth Reality What to check
Leased IPs are inferior Quality depends on reputation, routing and management, not only ownership. Blacklist status, route visibility, rDNS, geolocation, abuse history.
IPv4 leasing is only for startups Large companies also lease for flexibility, projects and regional growth. Contract term, renewal rules, escalation process, ASN compatibility.
IPv6 will remove IPv4 demand soon Dual-stack operation remains common because IPv6 adoption is uneven. Customer regions, partner networks, application dependencies.
All providers are the same Operational support can be the difference between quick deployment and weeks of delay. LOA handling, RPKI/ROA support, routing help, abuse process, reputation checks.

IPv4 leasing myth 1: leased IP addresses are lower quality

A leased IPv4 address is not automatically worse than a purchased IPv4 address. From the perspective of most users and online services, the important question is how the IP address behaves. If the prefix has clean reputation, valid routing, correct records and responsive abuse handling, its lease status is usually invisible in daily use.

Problems appear when a leased block has unresolved reputation debt, outdated geolocation, missing ROAs, inconsistent route objects or poor documentation. The same problems can also happen with owned address space. Ownership alone does not make a prefix clean.

Quality signals for IPv4 leasing

  • Clean DNSBL and security reputation checks.
  • Valid LOA and clear authority to announce the prefix.
  • Correct RPKI ROA records for the intended origin ASN.
  • Accurate route objects and registry information.
  • Reverse DNS support where the use case requires it.
  • Clear abuse contact and escalation path.
  • Geolocation review before production traffic starts.

IPv4 leasing myth 2: leasing is only for small companies

IPv4 leasing is attractive to smaller companies because it reduces upfront cost. But that does not make it a small-company-only model. Larger providers use IPv4 leasing when they need flexibility, faster access to resources or separation between projects, customers and regions.

A cloud provider may lease addresses to test a new geography. A hosting company may lease a clean /24 for a new customer segment. A SaaS platform may need separate address ranges for email, application traffic and security controls. In these cases, IPv4 leasing is not a sign of weakness. It is a way to match infrastructure capacity to actual business demand.

IPv4 leasing myth 3: IPv6 will make IPv4 leasing unnecessary soon

IPv6 growth is real and important. Still, IPv4 leasing remains relevant because many networks, customers and services continue to depend on IPv4 connectivity. Even organizations that support IPv6 often need dual-stack operation so that IPv4-only users can still reach them.

The practical strategy is not to ignore IPv6. The practical strategy is to plan for both realities: deploy IPv6 where possible and maintain reliable IPv4 reachability where customers, partners or legacy systems still require it.

IPv4 leasing myth 4: a leased IPv4 block can be taken away at any time

This fear usually comes from unclear contracts or unreliable suppliers. A reputable IPv4 leasing provider should define the lease term, renewal process, payment terms, acceptable use rules, abuse handling process and notice periods. When those terms are clear, IPv4 leasing can support stable long-term infrastructure planning.

Risk increases when a business leases from an informal source without proper documentation. Missing authority, unclear LOA terms or poor communication can delay routing, create provider disputes or lead to unexpected service interruption. The solution is not to avoid IPv4 leasing. The solution is to work with a provider that treats documentation as part of the product.

IPv4 leasing myth 5: once the prefix is delivered, the work is finished

Receiving an IPv4 block is only the beginning. The block must be prepared, announced, monitored and maintained. This is where many IPv4 leasing mistakes happen. A technically assigned range can still fail operationally if routing, DNS, geolocation or reputation are ignored.

Routing readiness

Check origin ASN, BGP visibility, route objects and RPKI/ROA before relying on the prefix.

Reputation readiness

Review blacklist status, abuse history and email deliverability before assigning the block to customers.

Geolocation readiness

Compare major geolocation databases and publish or update geofeed data when location accuracy matters.

IPv4 leasing myth 6: all IPv4 leasing providers are the same

IPv4 leasing providers can differ significantly. Some only provide access to an address block. Others help with authorization, routing coordination, RPKI, abuse handling and operational support. That difference matters when a business needs production-ready address space.

A low price can become expensive if the block triggers fraud filters, fails route validation, shows the wrong country, has unresolved blacklist history or lacks a responsive support channel. The total cost of IPv4 leasing includes the time required to make the block usable.

IPv4 leasing myth 7: IP reputation does not matter

IP reputation matters for many use cases, especially email, hosting, VPN, proxy, SaaS, security and customer-facing platforms. If an IPv4 block was previously associated with spam, phishing, malware, abusive proxy use or scanning, some services may continue to treat the range with caution after a lease begins.

Reputation is not fixed forever, but it must be managed. Businesses should check major blocklists, review abuse signals, monitor customer activity and respond quickly to complaints. For email use cases, reputation work should include SPF, DKIM, DMARC, reverse DNS, gradual warmup and bounce monitoring.

IPv4 leasing due diligence checklist

1. Verify documentation

  • Confirm the resource holder and authority to lease.
  • Review LOA terms and renewal conditions.
  • Check WHOIS or RDAP information.
  • Confirm abuse contact details.

2. Verify routing

  • Confirm the intended origin ASN.
  • Create or update RPKI ROAs.
  • Review route objects and maxLength.
  • Monitor BGP after announcement.

3. Verify reputation

  • Check DNSBL and security reputation tools.
  • Review historical abuse indicators where available.
  • Test email behavior before production use.
  • Monitor abuse reports after onboarding.

4. Verify geolocation

  • Check country and city results across providers.
  • Publish or update geofeed data if needed.
  • Submit correction requests to key databases.
  • Allow time for propagation.

How InterLIR helps with IPv4 leasing

InterLIR helps make IPv4 leasing operationally ready

InterLIR connects businesses with IPv4 leasing, purchasing and monetization options, while also paying attention to the practical issues that decide whether a prefix is usable in production: authorization, routing, reputation, geolocation and support.

For companies that need IPv4 address space, this reduces the risk of treating IPv4 leasing as a simple price-per-IP transaction.

Good IPv4 leasing is not just about receiving addresses. It is about receiving address space that can be announced, trusted, monitored and supported. That is where provider experience matters.

FAQ about IPv4 leasing myths

Is IPv4 leasing safe for business infrastructure?

IPv4 leasing can be safe for business infrastructure when the lease terms, authorization, routing, RPKI/ROA, reputation and support process are clear. The main risk is not leasing itself, but using poorly documented or poorly managed address space.

Are leased IPv4 addresses worse than purchased addresses?

No. Leased IPv4 addresses are not automatically worse than purchased addresses. A clean, well-routed leased prefix can work better than an owned prefix with poor reputation or outdated records.

Why do large companies use IPv4 leasing?

Large companies use IPv4 leasing for flexibility. It helps them expand capacity, test regions, isolate customer traffic, support migrations or avoid buying permanent address space before the business case is clear.

Will IPv6 end IPv4 leasing?

IPv6 will reduce long-term dependence on IPv4, but it has not made IPv4 leasing irrelevant. Many networks and services still require IPv4 reachability, so dual-stack planning remains common.

What should I check before leasing IPv4 addresses?

Before leasing IPv4 addresses, check ownership authority, LOA, WHOIS or RDAP records, RPKI/ROA, route objects, BGP visibility, DNSBL status, geolocation accuracy, reverse DNS support and abuse response process.

Conclusion: treat IPv4 leasing as an operational decision

The biggest IPv4 leasing myths come from focusing too much on ownership and too little on operations. Whether a block is leased or owned, businesses need clean reputation, correct routing, reliable documentation, active monitoring and responsive support.

For many organizations in 2026, IPv4 leasing is a practical way to access scarce address resources without heavy upfront investment. The best results come from choosing a provider that understands not only the IPv4 market, but also the operational details that make address space ready for real infrastructure.

Acquired IPv4 Reputation: Blacklists & Hidden Costs

The Hidden Costs of Acquired IPv4: Geolocation Mismatch, Blacklists and Reputation Debt

Acquired IPv4 reputation can determine whether a leased or purchased IP block is ready for production. Every prefix carries operational history: previous routing, outdated geolocation data, blacklist exposure, abuse reports and reputation signals.

For companies leasing, buying or transferring IPv4 resources, these hidden factors can affect email deliverability, user access, fraud checks, compliance reviews and infrastructure reliability.

The global shortage of IPv4 addresses has created an active secondary market. Companies lease, buy and transfer IPv4 blocks to support hosting, cloud infrastructure, SaaS platforms, email systems, VPN services, CDN deployments and other internet-facing services.

At first glance, acquiring IPv4 space may look like a straightforward process: verify the seller or lessor, receive a Letter of Authorization, update WHOIS or RDAP records, configure routing and start using the addresses.

In practice, an IPv4 block is not a blank technical asset. Previous routing, outdated geolocation data, DNSBL listings, abuse reports and poor IP reputation can follow the block after a transfer or lease.

Quick answer: the main hidden costs of acquired IPv4 are geolocation mismatch, blacklist exposure and reputation debt. These issues can disrupt access to online services, reduce email deliverability, trigger fraud filters and increase support workload after deployment.

Acquired IPv4 reputation is the combined effect of a prefix’s previous use, abuse history, blacklist status, geolocation records and routing background. Even when ownership or leasing documentation is correct, the wider internet may still evaluate the block based on its past.

This is why IPv4 acquisition should not be treated only as a pricing decision. Whether a company leases IPv4 addresses, buys a prefix for long-term use or prepares address space for customer-facing infrastructure, it needs a proper technical and reputation check before production traffic starts.

Key takeaways

1

Geolocation can lag

IPv4 geolocation may remain outdated for weeks or months after a prefix moves to a new country, network or provider.

2

Geofeeds reduce guesswork

Geofeeds give geolocation providers a structured source of prefix-to-location information.

3

Reputation follows the block

Transferred or leased IP space may inherit abuse history, blacklist records or poor email reputation.

4

Routing must be secured

RPKI/ROA, route objects and proper authorization help reduce routing and onboarding risks.

What “acquired IPv4” really means

In this article, acquired IPv4 means any IPv4 address space that an organization starts using after it was previously controlled, routed or used by another party.

Leased IPv4 prefixes
Purchased IPv4 blocks
Transferred resources
Brokered address space
Marketplace IPv4 deals
Customer-facing IP ranges

The commercial status of the block may change quickly, but the internet ecosystem does not update instantly. Geolocation databases, mail filters, security platforms, fraud systems and reputation tools may continue to treat the addresses according to their previous history.

This matters for companies using IPv4 space for real infrastructure. A prefix can be technically routed correctly and still cause business problems if banks, SaaS platforms, streaming services, mail providers or fraud prevention systems classify it incorrectly.

Risk map: where hidden IPv4 costs appear

Risk area What can go wrong Business impact
Geolocation The IP appears to be in the wrong country, region or city. Blocked access, fraud checks, wrong content region, customer complaints.
Blacklist history The prefix was previously associated with spam, malware, phishing or abuse. Email rejection, blocked traffic, security reviews and compliance delays.
Routing records ROAs, route objects or origin ASN records are missing, outdated or inconsistent. BGP issues, invalid announcements, failed provider verification.
Documentation LOA, WHOIS/RDAP or authorization details are incomplete. Deployment delays, failed onboarding and additional manual verification.

Geolocation mismatch: when an IP appears to be in the wrong country

IP geolocation databases do not work like GPS. They estimate location from a combination of signals, including WHOIS and RDAP records, routing data, traceroutes, user-submitted corrections, commercial datasets and geofeeds.

When a prefix is reallocated, transferred or announced from a new network, it may be operationally used in one country while still being listed in another country by major geolocation providers.

This creates an IPv4 geolocation mismatch: the network operator expects the block to be treated as one location, while websites, applications and security systems see a different location.

Common consequences of incorrect IP geolocation

  • Banking portals may block or challenge users because the IP appears to come from another country.
  • Streaming platforms may show the wrong content library or deny access.
  • Fraud prevention systems may flag legitimate sessions as suspicious.
  • Ad platforms and analytics tools may misclassify traffic.
  • Compliance-sensitive services may apply the wrong regional rules.
  • Support teams may receive complaints that are difficult to diagnose.

The problem becomes more visible in the IPv4 secondary market because prefixes move more often. A block that was previously routed in one region may later be leased to a customer in another region, transferred to a new holder or used by a different infrastructure provider.

For example, a company may lease a /24 for infrastructure in Germany, but parts of the internet may still classify the range as being located in another country. From the customer’s point of view, the service may look broken even though the routing is technically correct.

Why geolocation matters for IPv4 leasing and acquisition

Geolocation accuracy is especially important when IPv4 space is leased, purchased or transferred from another organization. The new user may receive valid technical documentation, but the wider internet may still associate the prefix with its previous location, previous routing history or previous abuse patterns.

This creates a gap between legal control and operational readiness. A company may be fully authorized to use a block, but still face problems with incorrect geolocation, DNSBL listings, outdated route objects, missing ROAs or poor reputation signals.

For IPv4 lessees

A leased prefix should be checked before customer traffic starts. Price matters, but routing readiness, geolocation accuracy and reputation history often matter more in production.

For IPv4 buyers

A purchased block can become a long-term asset, but only if the buyer understands its previous use, abuse history, registry status and operational condition.

For resource holders

Owners leasing out unused IPv4 space should keep documentation, route authorization and abuse handling clean to protect long-term asset value.

For businesses that depend on stable infrastructure, these issues can affect more than network configuration. They can influence customer access, email deliverability, fraud checks, compliance reviews and support workload.

Geofeeds: a practical way to reduce geolocation mismatch

A geofeed is a standardized CSV file that maps IP prefixes to geographic information such as country, region and city. The format is described in RFC 8805.

Instead of forcing every geolocation provider to infer location indirectly, a geofeed lets a network operator publish a structured declaration of where prefixes should be geolocated.

Example geofeed entry

203.0.113.0/24,DE,DE-BE,Berlin,

The exact data should match the operational reality of the network. For privacy and accuracy reasons, geofeeds should describe infrastructure or user groups at an appropriate level, not expose overly precise information about individual users.

Benefits of publishing a geofeed

Faster correction

Geolocation providers receive a clear and structured source instead of relying only on inference.

Lower support cost

Fewer users are blocked or misclassified because of stale location data.

Better operational control

The resource holder can maintain location data as prefixes are reassigned.

Cleaner onboarding

Newly leased, transferred or acquired IPv4 space can be prepared before production traffic begins.

For operators managing many IPv4 ranges, geofeeds should be part of the normal provisioning workflow. Whenever a prefix is leased, moved, transferred or reassigned, the geofeed should be reviewed and updated.

Signed geofeeds and RPKI

Publishing a geofeed is useful, but consumers also need to know that the file is legitimate. RFC 9632 describes how geofeed data can be discovered and how it can optionally be authenticated using RPKI.

A signed geofeed helps prove that the location information was published by the legitimate resource holder or an authorized party. This matters because incorrect geolocation data can affect access control, fraud systems, digital services and user trust.

Important: RPKI does not define IP geolocation by itself. RPKI helps validate routing authorization. Signed geofeeds use resource ownership signals to make geolocation data more verifiable.

Signed geofeeds are especially relevant for IPv4 leasing providers, hosting operators, networks with frequent customer reallocations and companies operating infrastructure across several countries.

Geofeeds do not guarantee instant correction across every provider. Each geolocation database has its own update process. Still, publishing a correct geofeed gives providers a clear, machine-readable source and reduces the time spent on manual correction requests.

For companies that lease or buy IPv4 resources, geofeeds should be combined with routing security. InterLIR explains the practical role of RPKI in IPv4 leasing and BGP security in its article What Is RPKI and Why It Matters for IPv4 Leasing, BYOIP, and BGP Security.

Acquired IPv4 reputation, blacklisting and reputation debt

Geolocation is only one side of the problem. The second hidden cost is IP reputation debt.

IP reputation debt means the negative operational history attached to an IP range before the new owner or lessee starts using it. This can include spam, phishing, malware hosting, botnet activity, bulletproof hosting, scanning, abusive proxy activity or previous route hijacking incidents.

DNS-based blocklists and reputation systems track IP addresses and ranges associated with abuse. When an IPv4 block changes hands, its legal or commercial ownership may change, but reputation systems may still remember the previous behavior. A clean transfer document does not automatically erase blacklist history.

Email deliverability

Messages may be rejected, throttled or routed to spam.

Network access

Firewalls and security platforms may block or challenge traffic.

Customer trust

Users may see warnings, failed logins or unusual verification prompts.

Operational delays

Delisting and remediation may take days or weeks.

Not every listing has the same meaning. Some lists indicate direct abuse. Others are policy-based, for example dynamic residential ranges that should not send mail directly. Some listings expire automatically after the activity stops, while others require manual delisting and evidence of remediation.

This is why reputation checks should be done before purchase, lease or production onboarding.

Why acquired IPv4 reputation can be riskier than expected

Transferred or leased IPv4 space should never be assumed clean without verification. The risk varies by prefix, region, previous user and intended use case, but the operational lesson is simple: a block’s past can affect its future value.

Why the risk exists

  1. Previous abuse may not be visible in basic WHOIS checks. A block can look valid in registry data while still having a poor reputation.
  2. Bad actors may try to reset reputation through new address space. Abusive operators often move between ranges after older prefixes become burned.
  3. Reputation systems lag behind ownership changes. Filters may continue to associate the range with the previous user.
  4. Inactive blocks can be abused after reactivation. A prefix that was quiet for months may attract attention when it suddenly starts sending traffic again.
  5. Routing and registry data may not align perfectly. Route objects, ROAs, origin ASNs and WHOIS records may require cleanup after transfer or lease activation.

For IPv4 buyers and lessees, this means that price per IP is only one part of the real cost. A cheaper block can become expensive if it requires urgent delisting, repeated geolocation correction, customer support escalation or onboarding delays.

Due diligence checklist before acquiring or leasing IPv4

The best time to identify hidden IPv4 costs is before the block is used in production. A structured due diligence process should cover ownership, authorization, routing, geolocation and abuse history.

1. Verify ownership and authorization

  • Check WHOIS and RDAP records.
  • Confirm organization and maintainer details.
  • Review the chain of title for transferred resources.
  • Obtain a proper Letter of Authorization where needed.
  • Confirm that the lessor, seller or marketplace is authorized to provide the range.

2. Check routing hygiene

  • Confirm the intended origin ASN.
  • Create or update RPKI ROAs before production announcement.
  • Review maxLength settings to avoid accidental RPKI-invalid announcements.
  • Check IRR route objects and remove outdated routing records where possible.
  • Monitor BGP visibility after the prefix goes live.

3. Audit IP reputation

  • Check major DNSBLs and security reputation services.
  • Review historical abuse indicators where available.
  • Check whether the range was associated with spam, malware, phishing or proxy abuse.
  • Test email deliverability before assigning the range to mail infrastructure.
  • Document all findings before accepting the block for production use.

4. Audit geolocation

  • Compare the prefix across multiple geolocation providers.
  • Identify incorrect country, region or city data.
  • Publish or update a geofeed before customer traffic starts.
  • Add the geofeed reference in WHOIS or RDAP where supported.
  • Submit corrections directly to key geolocation providers when needed.

5. Prepare DNS and email foundations

  • Configure reverse DNS where applicable.
  • Set SPF, DKIM and DMARC for domains that will send mail.
  • Avoid using newly acquired space for high-volume email immediately.
  • Warm up email traffic gradually and monitor bounce patterns.
  • Keep abuse contact information accurate and responsive.

6. Use a staged production rollout

  • Start with low-risk services before critical workloads.
  • Monitor logs for blocked traffic, login challenges and user complaints.
  • Track blacklist status during the first weeks.
  • Keep a rollback plan ready if the range causes service disruption.
  • Allow time for geolocation and reputation corrections to propagate.

How InterLIR helps reduce hidden IPv4 costs

InterLIR helps make IPv4 resources usable, not just available

InterLIR is an IPv4 marketplace for companies that need to lease, buy, sell or monetize IPv4 resources. But the value of an IPv4 block is not limited to its price or availability. The block also needs to be operationally ready.

That means checking authorization, routing records, geolocation consistency and reputation risks before the prefix is used in production.

For companies leasing or acquiring IPv4 space, InterLIR helps reduce the operational friction that often appears after the transaction:

IPv4 leasing and marketplace access

Companies can access available IPv4 blocks through a structured marketplace model instead of relying on informal or poorly documented arrangements.

Authorization and documentation

Proper LOA handling, WHOIS/RDAP checks and resource-holder verification help reduce onboarding delays and ownership confusion.

Routing readiness

Route objects, RPKI/ROA and origin ASN checks help ensure the prefix is technically ready for announcement.

Geolocation support

Geolocation review and correction workflows help reduce wrong-country classification and related customer-facing issues.

Reputation awareness

Blacklist and abuse-history awareness helps customers avoid assigning problematic address space to sensitive workloads too quickly.

Operational continuity

A more structured IPv4 process reduces the chance that hidden issues appear only after production traffic starts.

For companies that need IPv4 space quickly, InterLIR IPv4 leasing provides access to available IPv4 blocks through a marketplace model. For IP resource holders, leasing out IPv4 addresses through InterLIR can turn unused IPv4 space into recurring revenue while keeping the process organized.

If an acquired or leased prefix will later be used in a cloud environment, InterLIR BYOIP can also help with IP-side preparation. However, BYOIP is only one possible use case. The broader issue is making sure the IPv4 block is clean, authorized, correctly routed and ready for real infrastructure.

How to prepare acquired IPv4 before production use

Before a leased or purchased IPv4 block is assigned to customers, applications or production infrastructure, operators should verify that the prefix is ready from several angles.

Preparation step Why it matters What to check
Authorization Confirms that the announcing party is allowed to use the prefix. LOA, resource holder, lessor or seller, registry records.
Routing Prevents invalid announcements and routing conflicts. Origin ASN, RPKI ROA, IRR route objects, BGP visibility.
Geolocation Reduces wrong-country classification and service disruption. Major geolocation providers, geofeed, WHOIS/RDAP references.
Reputation Protects email, access control and customer-facing services. DNSBL status, abuse history, mail reputation, traffic patterns.
Rollout Limits the impact if a hidden issue appears. Low-risk testing, monitoring, rollback plan, support readiness.

FAQ: acquired IPv4, geolocation and blacklists

What is IPv4 reputation debt?

IPv4 reputation debt is the negative history attached to an IP range before a new owner or lessee starts using it. It may include spam, malware, phishing, proxy abuse, scanning, botnet activity or previous blacklist listings.

Can a geofeed instantly fix incorrect IP geolocation?

No. A geofeed gives geolocation providers a structured source of information, but each provider updates its database on its own schedule. A geofeed reduces uncertainty and manual work, but it does not guarantee instant global correction.

Does RPKI fix IP geolocation?

No. RPKI helps validate whether an ASN is authorized to originate a prefix. It improves routing security. Geolocation is handled separately through geolocation databases, geofeeds and provider correction processes.

Should acquired IPv4 be used for email immediately?

Usually not. Email is highly sensitive to IP reputation. Before using acquired IPv4 for mail, check DNSBLs, configure reverse DNS, set SPF, DKIM and DMARC, test deliverability and warm up sending volume gradually.

Why is InterLIR relevant to this topic?

InterLIR works with IPv4 leasing, buying, selling and operational preparation of IPv4 resources. These are exactly the scenarios where hidden IPv4 costs appear: geolocation mismatch, blacklist exposure, routing inconsistencies and reputation debt.

Conclusion

IPv4 scarcity has turned address blocks into valuable assets, but acquired IPv4 space can carry hidden operational costs.

Geolocation mismatch can break user access, trigger fraud systems and generate support tickets. Reputation debt can damage email deliverability, network access and customer trust. Routing inconsistencies can create additional risk if RPKI, IRR and WHOIS records are not updated correctly.

The solution is not to avoid the IPv4 market. The solution is to treat IPv4 acquisition as an operational risk process, not only a commercial transaction.

Before using purchased or leased IPv4 space, verify ownership, audit reputation, publish geofeeds, configure RPKI/ROA and plan a staged rollout. With proper preparation, acquired IPv4 can become a reliable infrastructure asset instead of a source of preventable problems.

Need IPv4 space without hidden operational surprises?

InterLIR helps companies lease, buy and prepare IPv4 resources with attention to authorization, routing, geolocation and reputation risks.

Lease IPv4 addresses
Talk to InterLIR

Related InterLIR resources

Rent IPv4 Addresses with InterLIR
Lease Out IPv4 Addresses
What Is RPKI and Why It Matters
InterLIR BYOIP

What Is RPKI and Why It Matters for IPv4 Leasing, BYOIP, and BGP Security

RPKI, or Resource Public Key Infrastructure, is one of the most important routing security technologies used on today’s Internet. It helps IP resource holders prove which Autonomous System is authorized to originate their IP prefixes, reducing the risk of unauthorized BGP announcements, route hijacks, and accidental routing failures.

The Internet depends on thousands of independent networks exchanging reachability information through the Border Gateway Protocol, better known as BGP. BGP makes global routing possible, but its original trust model did not include strong cryptographic verification of whether a network was actually allowed to announce a specific IP prefix. RPKI was developed to close part of that gap.

Key idea: RPKI does not replace BGP. It adds a cryptographic authorization layer that helps networks check whether the origin ASN in a BGP route is authorized to announce a specific IP prefix.

What Is RPKI?

RPKI stands for Resource Public Key Infrastructure. It is a public key infrastructure designed specifically for Internet number resources, including IP address blocks and Autonomous System Numbers.

Unlike the Web PKI, which is mainly used to validate domain names and website identities, RPKI validates statements about Internet routing resources. In practical terms, it allows the holder of an IP prefix to create a signed authorization showing which ASN may originate that prefix in BGP.

This signed authorization is called a Route Origin Authorization, or ROA. Network operators can then use Route Origin Validation, or ROV, to compare BGP announcements against validated ROA data.

Why RPKI Matters for Internet Routing

Without RPKI, a network may accidentally or deliberately announce IP space that belongs to another organization. If other networks accept that route, traffic can be redirected, dropped, degraded, or exposed to interception risks.

RPKI helps reduce this risk by giving resource holders a way to publish cryptographically verifiable routing intent. When a route is inconsistent with the published authorization, networks that perform Route Origin Validation can reject it or treat it with lower preference.

  • It helps prevent unauthorized origin announcements.
  • It reduces the operational impact of BGP misconfigurations.
  • It gives IP holders more control over how their prefixes are originated.
  • It supports safer multi-homing, Anycast, cloud, CDN, and DDoS protection setups.
  • It improves routing hygiene across the global Internet.

How RPKI Works

RPKI follows the allocation hierarchy of Internet number resources. IP addresses and ASNs are distributed through IANA, Regional Internet Registries, National Internet Registries, Local Internet Registries, and resource holders. RPKI certificates reflect that resource hierarchy.

A resource certificate confirms that a holder has been allocated or assigned specific IP resources. The certificate itself does not define routing policy. Instead, it allows the resource holder to create signed objects, especially ROAs, that describe which ASN is allowed to originate a prefix.

RPKI Component What It Does Why It Matters
Resource certificate Confirms control over IP address space or ASNs within the RPKI hierarchy Provides the cryptographic foundation for signed routing statements
ROA Authorizes a specific ASN to originate one or more IP prefixes Lets networks verify whether a BGP origin announcement is legitimate
RPKI repository Publishes certificates, ROAs, manifests, CRLs, and related objects Makes routing authorization data available to relying-party validators
Relying-party validator Fetches and validates RPKI data from repositories Produces validated prefix-origin data for network operators
Router using ROV Compares BGP routes against validated RPKI data Can accept, reject, or de-preference routes based on validation state

What Is a ROA?

A ROA, or Route Origin Authorization, is a digitally signed object that states which Autonomous System is authorized to originate a particular IP prefix or group of prefixes.

A typical ROA includes three key elements: the IP prefix, the authorized origin ASN, and the maximum prefix length that may be announced. For example, a resource holder might authorize AS64496 to originate 203.0.113.0/24. If more specific announcements are allowed, the ROA may include a maximum length such as /25 or /26.

Important: The maximum length field must be configured carefully. If it is too broad, it may authorize more specific announcements than intended. If it is too narrow, legitimate announcements can become RPKI-invalid.

For IP resource holders, ROA accuracy is critical. A wrong origin ASN, an incorrect maximum length, or a forgotten ROA update after a network change can cause legitimate routes to be marked Invalid by networks that enforce RPKI validation.

Route Origin Validation: Valid, Invalid, and NotFound

Route Origin Validation is the process of checking a BGP announcement against validated RPKI data. The result normally falls into one of three states: Valid, Invalid, or NotFound.

Validation State Meaning Typical Operational Response
Valid The route matches a ROA: the origin ASN is authorized and the prefix length is permitted. The route can be accepted according to the operator’s normal routing policy.
Invalid A covering ROA exists, but the route does not match the authorized ASN or allowed prefix length. Many operators reject the route or assign it a lower preference.
NotFound No relevant ROA exists for the prefix. The route is usually treated differently from Invalid; NotFound does not automatically mean malicious.

The distinction between Invalid and NotFound is important. Invalid means there is a relevant authorization record and the route conflicts with it. NotFound simply means there is no matching ROA. Since RPKI deployment is still not universal, many routes may remain NotFound.

RPKI Repositories, Validators, and Routers

Routers usually do not perform all RPKI cryptographic validation themselves. Instead, relying-party software fetches RPKI objects from repositories, validates them, and produces a set of validated prefix-origin records.

Routers then receive this validated data through the RPKI-to-Router protocol. This design keeps heavy cryptographic processing away from routers while still allowing routing policy to use RPKI validation results.

RPKI repositories were historically fetched using rsync, but RRDP, the RPKI Repository Delta Protocol, was introduced to improve scaling. RRDP uses HTTPS-based snapshots and deltas, making it better suited to caching and large-scale distribution.

RPKI vs IRR: What Is the Difference?

RPKI and Internet Routing Registries are both used in routing policy, but they are not the same. IRR data is widely used to build prefix filters and document routing intent, while RPKI adds cryptographic validation tied to Internet number resources.

Area IRR RPKI
Main purpose Publishes routing policy and route objects Cryptographically authorizes route origin
Trust model Depends on registry quality, maintainer controls, and operational discipline Follows the resource certificate hierarchy
Common object route / route6 object ROA
Operational use Prefix filter generation and routing policy documentation Route Origin Validation
Best practice Keep route objects accurate where required by peers or upstreams Create accurate ROAs and monitor validation status

In modern network operations, RPKI and IRR often coexist. Many upstreams and peers still use IRR data, while RPKI is increasingly expected for origin validation and routing security.

What RPKI Protects Against

RPKI is especially useful against unauthorized route origination. If an attacker or misconfigured network announces a prefix from an ASN that is not authorized in the ROA, networks enforcing Route Origin Validation can identify the route as Invalid.

  • Accidental prefix hijacks caused by configuration errors
  • Deliberate BGP origin hijacks
  • Some cases of incorrect route propagation
  • Misaligned routing after ASN changes or provider migrations
  • Operational mistakes involving more-specific announcements

This is why RPKI is important for ISPs, cloud providers, hosting companies, enterprises, CDNs, DDoS protection networks, and organizations using multi-homed or Anycast infrastructure.

What RPKI Does Not Solve

RPKI is powerful, but it is not a complete solution for all BGP security problems. Its most widely deployed function is origin validation. That means it checks whether the origin ASN is authorized to announce a prefix, not whether the full AS path is legitimate.

Because of this, RPKI by itself cannot fully prevent all route leaks, AS path manipulation, or policy violations. Other mechanisms and operational controls are still needed, including prefix filtering, peer review, monitoring, routing policy hygiene, and emerging technologies such as ASPA.

Practical view: RPKI should be treated as a core routing security layer, not as a single complete security system. It reduces an important class of BGP risks, but it must be combined with sound routing operations.

Common RPKI Mistakes

Most RPKI problems are operational rather than conceptual. The technology is designed to improve routing security, but incorrect records can create real reachability problems.

  • Creating a ROA for the wrong origin ASN
  • Setting the maximum prefix length too narrowly
  • Setting the maximum prefix length too broadly
  • Forgetting to update ROAs after changing transit providers
  • Announcing more-specific prefixes that are not covered by ROAs
  • Not checking validation status before a routing migration
  • Assuming NotFound means malicious or Invalid means always malicious
  • Failing to coordinate ROAs with IRR route objects and upstream filters

For businesses that lease IPv4 addresses, use BYOIP, migrate providers, or route prefixes through multiple networks, RPKI should be included in the change management process. A routing change should not be considered complete until ROAs, route objects, upstream filters, and monitoring have been checked.

RPKI Checklist for IP Resource Holders

Before creating or updating ROAs, IP resource holders should confirm the routing plan and the authorization chain. This is especially important when using leased IPv4 ranges, multiple upstreams, Anycast, or cloud and CDN providers.

Recommended RPKI checklist:
  • Confirm which ASN or ASNs will originate each prefix.
  • Confirm the exact prefix lengths that will be announced.
  • Set ROA maximum length only as broad as operationally required.
  • Check whether IRR route objects also need to be updated.
  • Validate the route before and after BGP changes.
  • Monitor Valid, Invalid, and NotFound states after deployment.
  • Include ROA updates in provider migration and BYOIP workflows.
  • Document who is responsible for future RPKI changes.

RPKI and BYOIP

RPKI is increasingly relevant in BYOIP projects. When a company brings its own IP prefix to a cloud, CDN, hosting, or DDoS protection provider, the provider may need to confirm that the prefix can be safely originated or used in its infrastructure.

A correct ROA can show which ASN is authorized to originate the prefix. If the ROA is missing, too restrictive, or points to the wrong ASN, the BYOIP onboarding process may fail or the route may be rejected by networks that enforce RPKI validation.

For leased IPv4 ranges, this becomes even more important. The organization using the range must ensure that the lease terms, authorization documents, registry data, route objects, ROAs, and provider-specific requirements all support the intended routing setup.

Need IPv4 Ranges Prepared for BYOIP or Routing?

InterLIR helps businesses lease IPv4 ranges and prepare the IP-side configuration needed for routing, BYOIP, RPKI/ROA coordination, route objects, LOA documentation, WHOIS/RDAP updates, and verification steps where applicable.

Explore InterLIR BYOIP Solutions

The Future of RPKI

RPKI has moved from a specialized routing security technology to a mainstream part of Internet operations. More networks are publishing ROAs, more operators are validating routes, and routing security initiatives increasingly treat RPKI as a baseline practice.

The next stage of routing security is likely to involve broader automation, better monitoring, cleaner operational tooling, and complementary technologies that address route leaks and AS path validation. ASPA, or Autonomous System Provider Authorization, is one emerging direction that aims to improve protection against route leaks and certain AS path problems.

RPKI does not make BGP perfectly secure, but it significantly improves one of BGP’s weakest points: the lack of cryptographic proof that an ASN is authorized to originate a prefix. For any organization that manages IP resources, RPKI is no longer optional knowledge. It is part of modern routing hygiene.

RPKI FAQ

What does RPKI mean?

RPKI means Resource Public Key Infrastructure. It is a security framework for Internet number resources that allows IP prefix holders to publish cryptographically signed routing authorizations.

What is a ROA?

A ROA, or Route Origin Authorization, is a signed object that authorizes an Autonomous System to originate one or more IP prefixes.

What is Route Origin Validation?

Route Origin Validation is the process of checking a BGP route against validated RPKI data. The route is usually classified as Valid, Invalid, or NotFound.

Does RPKI prevent all BGP hijacks?

No. RPKI helps prevent unauthorized origin announcements, but it does not validate the full AS path by itself. It should be combined with other routing security practices.

Is NotFound the same as Invalid?

No. Invalid means a relevant ROA exists but the route does not match it. NotFound means no relevant ROA was found. Many operators treat Invalid routes much more strictly than NotFound routes.

Can a wrong ROA break legitimate routing?

Yes. A wrong origin ASN or maximum prefix length can make legitimate routes appear Invalid to networks that perform Route Origin Validation.

Is RPKI important for BYOIP?

Yes. Many BYOIP workflows depend on correct routing authorization. A cloud, CDN, hosting, or network provider may require ROA updates before accepting or announcing a prefix.

Conclusion

RPKI is one of the clearest and most practical improvements to global Internet routing security. It gives IP resource holders a cryptographic way to state which ASN is authorized to originate a prefix and gives network operators a way to detect unauthorized or misconfigured announcements.

For ISPs, hosting providers, enterprises, cloud users, CDN deployments, DDoS protection setups, and organizations using leased IPv4 space, RPKI should be part of everyday routing operations. Correct ROAs, accurate route objects, careful provider coordination, and ongoing monitoring all help reduce avoidable routing risk.

RPKI does not solve every BGP security problem, but it addresses a fundamental weakness: verifying whether a route’s origin ASN is authorized. As Internet infrastructure becomes more complex and more security-sensitive, that verification is increasingly essential.

AI Hype as a New Argument in the IPv4 Market: What Transfer Data Shows So Far

AI has become one of the newest arguments in the IPv4 market. As artificial intelligence becomes more visible across the public Internet, more commentators are linking AI growth to renewed demand for IPv4 address space.

The logic is easy to understand. Chatbots, autonomous agents, AI search tools, crawlers, automation platforms, data collection systems and distributed inference services all need to interact with existing online infrastructure. A large part of that infrastructure still depends on IPv4, so it is tempting to assume that AI growth should automatically translate into stronger IPv4 demand.

The argument is plausible. But plausibility is not the same as proof.

At InterLIR, our view is that AI is relevant to the IPv4 market, especially for leasing, proxy infrastructure, outbound connectivity and reputation-sensitive routing. However, the available March-April 2026 transfer data does not yet prove that AI has directly reshaped the IPv4 purchase market or caused broad repricing.

Key takeaway

AI may increase the operational value of clean, routable IPv4 access. But current transfer data supports a more cautious conclusion: AI is a supporting demand factor, not yet a proven primary driver of IPv4 purchase-market growth.

  • AI-related use cases are real, especially for crawling, automation, proxy infrastructure and distributed outbound traffic.
  • Transfer data does not yet show an AI-led purchasing wave. April 2026 volume was driven mainly by larger transfers, not by a surge in small flexible blocks.
  • Leasing is likely to feel the AI effect first. Flexible access is often more useful than permanent ownership for temporary or scalable workloads.
  • The market is stabilising, not breaking out. Current data points to liquidity and a firmer floor, not confirmed broad repricing.

Why AI became part of the IPv4 market story

The AI-IPv4 argument is usually built on four assumptions.

  • AI applications need access to IPv4-only and dual-stack resources. Many websites, APIs, enterprise systems and legacy services still depend on IPv4.
  • Large-scale data collection may require distributed outbound traffic. Crawlers, agents and automation platforms may need IP diversity, geographic routing and reputation management.
  • Agent-based systems can generate more automated requests than traditional human users. This may increase demand for scalable network access.
  • AI-related workloads often prefer flexibility. Companies may lease or temporarily access IPv4 space instead of committing to permanent ownership.

Taken together, these assumptions support a credible market argument: AI may increase the operational value of clean, routable IPv4 address space, especially where reputation, geography and flexible access matter.

However, this argument should not be treated as direct evidence of a broad repricing of the IPv4 market.

The commercial interest behind the AI-IPv4 argument

There is also a commercial reason why this argument is gaining visibility.

Many participants in the IPv4 ecosystem benefit from presenting AI as a new structural driver of demand. Sellers benefit from a narrative that reduces pressure to discount. Leasing platforms benefit from positioning IPv4 as a flexible infrastructure layer for AI, automation and distributed workloads. Brokers benefit when buyers believe that current prices may represent an attractive entry point before future demand increases.

This does not mean the argument is false. It means the argument should be tested against observable data.

The strongest version of the AI-related IPv4 argument is not that every chatbot or AI agent needs its own dedicated public IPv4 address. That would be too simplistic. Public IP addresses are not reliable identity units for autonomous agents. Many agents can operate behind shared infrastructure, NAT, cloud gateways, proxy layers or API-based authentication systems.

The more realistic argument is narrower: AI-related workloads may increase demand for publicly routable IPv4 access, especially for outbound Internet connectivity, crawling, API interaction, proxy infrastructure, reputation-sensitive routing and temporary scaling.

That distinction matters. It separates a credible infrastructure effect from an overstated scarcity argument.

InterLIR’s view: no direct evidence yet of AI-driven IPv4 repricing

At InterLIR, our position is that the growth of AI agents, chatbots and automation systems is relevant to the IPv4 market. But current data does not yet prove a direct causal link between AI growth and higher prices in the IPv4 purchase market.

The available March and April 2026 transfer data shows stabilisation, continued liquidity and larger transfers. It does not yet show a clear AI-specific shift in purchasing activity.

Methodology note

Public IPv4 transfer data shows the movement of address space, but it does not disclose individual transaction prices. For this analysis, several records that appeared to represent the same transfer between the same parties, on the same date and under the same transfer category were treated as one observed transaction.

This means the analysis is useful for understanding transfer volume and structure, but it should not be read as direct transaction-level pricing data.

What changed between March and April 2026

On InterLIR’s adjusted transaction-counting basis, total transferred IPv4 volume increased from 3,626,496 addresses in March to 4,863,488 addresses in April. That is a material increase of about 34.1%.

However, April was not a month of broader market activity. It was mainly a month of larger transfers.

Metric March 2026 April 2026 Change
Total transferred IPv4 volume 3,626,496 addresses 4,863,488 addresses +34.1%
Observed transactions 331 312 -5.7%
Average transaction size About 10,956 addresses About 15,588 addresses +42.3%
/17-/20 transferred volume 811,008 addresses 2,035,712 addresses +151.0%
/24 transferred volume 70,656 addresses 37,376 addresses -47.1%
M&A-related transfer volume 633,088 addresses 1,528,576 addresses +141.4%

This structure is important. More address space changed hands in April, but through fewer and larger deals. The strongest increase came from the /17-/20 segment, while /24 volume declined sharply.

That weakens the argument that April’s higher transfer volume was driven by flexible, small-block demand. Many AI-related use cases discussed in the market, including proxy pools, temporary access, distributed outbound traffic and reputation-sensitive routing, would normally be expected to support demand for smaller and easily deployable blocks. April did not show a clear increase in that segment.

The role of M&A also became more visible

The role of M&A and corporate restructuring increased significantly in April. M&A-related transfer volume rose from 633,088 addresses in March to 1,528,576 addresses in April. Its share of total transferred volume increased from about 17.5% to about 31.4%.

This makes it difficult to read April’s higher volume as direct evidence of new AI-driven buying pressure. A significant part of the increase appears to reflect corporate, structural or portfolio-related movement rather than broad open-market demand from AI infrastructure buyers.

In short, the headline volume number looks strong. But the composition of that volume tells a more cautious story.

What the transfer data actually supports

The transfer data supports several careful conclusions.

  1. The IPv4 market remains active. Large blocks are still moving, and buyers are present for meaningful volumes of address space.
  2. The market appears to be stabilising after the 2025 correction. April’s higher total volume points to liquidity, but not necessarily to rising prices.
  3. The buyer base remains diversified. Telecom operators, hosting companies, data infrastructure providers, security companies, cloud-related businesses and corporate network operators continue to appear in transfer data.
  4. AI companies are not visibly dominating purchases. Current public transfer data does not show AI companies or AI-agent infrastructure providers as the clear leading buyer category.
  5. The decline in /24 volume matters. It makes it harder to argue that flexible small-block demand has already become a visible purchase-market driver.

These conclusions do not dismiss AI as irrelevant. They simply keep the argument grounded in observable evidence.

Where AI may still matter

AI should not be ignored. The growth of automated systems, AI crawlers, agentic workflows and machine-to-machine web interaction can increase the operational need for public IPv4 access.

This is especially relevant when systems need to interact with IPv4-only services, avoid excessive concentration of traffic behind a small number of addresses, manage IP reputation or distribute outbound traffic geographically.

However, this impact is more likely to appear first in leasing, proxy infrastructure, short-term address access and reputation-sensitive routing than in large-scale permanent purchases.

The likely AI impact path

  • First: stronger utilisation of leased IPv4 space and proxy infrastructure.
  • Second: more demand for clean, reputation-sensitive routing and geographically diverse access.
  • Third: possible support for a firmer market floor if AI-related workloads become sustained and measurable.
  • Not proven yet: broad AI-driven repricing of permanent IPv4 ownership.

AI-related demand may also be partially hidden inside broader infrastructure categories. Cloud providers, hosting companies, security platforms and data infrastructure operators may buy or lease address space for mixed workloads, including AI-related customers, without those transactions appearing in public data as explicitly AI activity.

This is a real limitation of the data. The absence of a visible AI buyer category does not prove that AI has no effect. But it also does not support the stronger claim that AI has already reshaped the purchase market.

Leasing may be the first place to watch

Public leasing commentary in 2026 continues to describe the leasing segment as more resilient than the purchase market, with rates broadly around the $0.40-$0.50 per IP per month range depending on region, quality and platform. At the same time, increased available supply may create pressure on less differentiated or lower-reputation space.

This is consistent with a more nuanced view of AI demand. AI may support demand for IPv4 usage without immediately causing a broad increase in IPv4 asset prices.

In practice, AI-related workloads may help increase utilisation of leased address space, reduce sellers’ willingness to discount further, or help establish a firmer price floor. But that is different from proving that AI has already triggered a new rally in the IPv4 purchase market.

Conclusion: AI is relevant, but not yet decisive

The current AI-related argument around IPv4 has a real underlying mechanism, but it should be treated carefully.

AI agents, chatbots, crawlers and automation systems are likely to increase demand for IPv4 access in specific operational contexts. The strongest current impact is likely to be in leasing, proxy infrastructure, distributed outbound connectivity, temporary scaling and clean-address reputation.

However, the March-April 2026 transfer data does not yet support the stronger claim that AI growth has directly reshaped the IPv4 purchase market or caused broad repricing. April’s increase in total transferred volume was driven mainly by large and mid-large transfers, while /24 volume declined and M&A-related activity became more prominent.

The most accurate position is this: AI is a relevant supporting demand factor, but not yet a proven primary driver of growth in the IPv4 purchase market.

For now, AI should be viewed as one of several forces helping to stabilise the market and potentially establish a firmer price floor, rather than as confirmed evidence of a new sustained upward cycle in IPv4 purchase prices.

Planning your IPv4 strategy around AI, automation or scaling demand?

InterLIR can help you evaluate IPv4 block quality, compare leasing and ownership economics, and choose the right access model for your infrastructure needs.

Talk to InterLIR about your IPv4 strategy

The IPv4 market in 2025: The great correction and the end of the “golden addresses” era

For years, the IPv4 address market felt like a never-ending bidding war. Scarcity looked permanent, prices above $50 per address no longer seemed unusual, and many buyers treated every available block as something to grab before someone else did.

Then 2025 changed the mood completely.

The market entered one of its sharpest corrections in more than a decade. Prices moved down, especially for larger blocks, while transfer activity remained strong. In other words, demand did not disappear. The market simply became more liquid, more selective, and far less emotional.

Key takeaways

  • Large-block supply changed the pricing dynamic. /16 and larger blocks became more available, reducing the urgency premium.
  • Buyers became more disciplined. Reputation, RIR region, transfer history, and clean provenance now matter more than raw scarcity.
  • Leasing stayed resilient. Many operators now prefer flexible access over large upfront CAPEX.
  • The market is not dying. It is maturing into a more rational, quality-driven IPv4 economy.

1. A supply surge killed the urgency premium

The biggest driver of the correction was the visible increase in large-block supply, especially /16 and larger allocations. When these lots started appearing more regularly, buyers no longer had to act as if every opportunity was their last.

The market shifted from a frantic auction environment to something much closer to a buyer’s market. There was more choice, more room for negotiation, and more time for proper due diligence.

The old mindset, “buy it now before it disappears,” has largely lost its power. In 2025, buyers started asking better questions: Where is the block registered? What is the abuse history? Is the geolocation clean? Are there blacklist issues? How smooth will the transfer be?

That shift matters. IPv4 is still scarce, but scarcity alone is no longer enough to justify panic pricing.

2. Technical workarounds are reducing pressure

Buying clean IPv4 addresses outright is no longer the only way to support growth. Operators have become more sophisticated, and several practical alternatives now reduce the pressure to overpay for ownership.

  • CGNAT and proxy architectures help networks use existing IPv4 space more efficiently.
  • IPv6-first deployment is becoming more realistic in environments where applications, users, and partners can support it.
  • IPv4 leasing has become a practical option for public-facing endpoints, legacy systems, B2B integrations, reputation-sensitive hosting, iGaming, anti-fraud platforms, and other use cases where IPv4 is still required.

This does not mean IPv4 is becoming obsolete. Far from it. But demand is becoming more selective. Businesses still need IPv4 in specific operational scenarios, but many are no longer willing to pay a heavy ownership premium just to hold addresses forever.

3. The financial logic of ownership changed

In 2021–2023, holding IPv4 looked like a strong CAPEX decision. Prices were climbing, scarcity was the dominant story, and many organizations believed that buying addresses was safer than leasing them.

By 2025, that logic became much less straightforward.

Segment 2025 market behavior What it means
Large blocks (/16+) Sharpest price correction, with some reports showing multi-year lows and sub-$20/IP levels in 2025. Buyers gained leverage, especially in larger transactions.
Smaller blocks (/24–/22) Generally more resilient and more dependent on RIR region, reputation, and clean history. Quality small blocks can still command a premium.
Leasing Remained comparatively stable, often around the $0.38–$0.45/IP/month range depending on region and platform. For many teams, leasing became the more flexible operating model.

The result is a different kind of calculation. If a company buys IPv4 at a high per-address price, the break-even period against leasing can stretch for years. For teams that need flexibility, short-term capacity, or predictable operating expenses, leasing or hybrid models can make more sense than permanent ownership.

Ownership still has a place, especially for organizations with long-term infrastructure needs, stable routing requirements, and strict control over reputation. But it is no longer the automatic best answer.

4. 2026 outlook: quality over quantity

The most likely scenario for 2026 is not a collapse and not a return to the old boom. The more realistic outlook is stabilization with clear market bifurcation.

The premium segment

Clean blocks with strong reputation, accurate geolocation, good RIR positioning, low abuse history, and transparent transfer records should remain attractive. These assets may hold value better, especially when buyers need certainty and speed.

The commodity segment

Average-quality, large, or problematic blocks may continue to face pricing pressure. If a block carries reputation issues, unclear provenance, blacklist problems, or transfer complexity, buyers now have more alternatives and less reason to accept risk.

This is the real lesson of 2025: the market is no longer rewarding passive hoarding in the same way. The winners will be the players who add operational value.

  • Fast and transparent transfers
  • Clear provenance and ownership history
  • Reputation checks and blacklist screening
  • Flexible leasing and short-term options
  • Support with RIR procedures, LOA, RPKI, reverse DNS, and routing documentation

Bottom line: IPv4 is not dead. Speculation is weaker.

The IPv4 “gold rush” is over, but the market is not dying. It is becoming more professional, more liquid, and more selective.

Demand remains healthy because many networks, platforms, and applications still depend on IPv4. At the same time, buyers are more careful, leasing is more accepted, and IPv6 is slowly changing the long-term planning picture.

If you are holding IPv4 addresses, the priority should be quality, documentation, and reputation. If you are buying or expanding, this may be one of the best windows in years to secure the resources you need without the panic pricing of the previous cycle.

The era of endless price increases is behind us. Welcome to the new, more rational IPv4 market.

Need a smarter IPv4 strategy for 2026?

Whether you are buying, selling, leasing, or evaluating your current IPv4 portfolio, InterLIR can help you understand market conditions, assess block quality, and choose the right model for your infrastructure needs.

Contact InterLIR to discuss your IPv4 options

Internet Censorship: Blocking, VPN Growth, and Rising Demand for IP Addresses

In recent years, the internet has become less free around the world. This trend is reflected not only in high-profile cases of complete internet shutdowns, but also in the systematic expansion of government control mechanisms — from restrictions on individual platforms to stricter legislation governing users and service providers. Internet censorship has become systemic, affecting both users and international platforms. This has inevitably led to increased demand for VPN services and IP addresses.

Service Interruptions and Restrictions

According to Freedom House, global internet freedom has declined for the fourteenth consecutive year. The Freedom on the Net 2024 report documents a deterioration in conditions in 27 of the 72 countries surveyed. This includes the expansion of censorship practices, increased pressure on technology companies, criminal prosecution for online speech, and manipulation of the digital information environment, particularly during election periods. Even in countries where direct bans are not imposed, mechanisms of control and surveillance continue to expand.
Another significant trend is the rise in so-called internet shutdowns — deliberate disruptions or severe restrictions on internet access imposed by authorities. The Access Now coalition reports that in 2024 alone, at least 296 such incidents were recorded across 54 countries. This represents one of the highest annual totals since systematic monitoring began in the mid-2010s. Shutdowns most commonly occur in the context of protests, elections, or armed conflicts.
At the same time, the nature of these restrictions is evolving. Whereas authorities previously often resorted to complete nationwide shutdowns, they are now increasingly employing more targeted measures. These include blocking specific social media platforms and messaging apps, throttling traffic to particular services, restricting VPN access, and imposing regional or temporary bans. Such measures are harder to detect and challenge, yet their impact on freedom of expression and access to information can be equally significant.
Overall, the trend of recent years is clear: state interference in the digital sphere is intensifying. Although the scale and forms of restrictions vary by region, aggregated international data point to a sustained global increase in internet censorship and service-blocking practices.

Growth in Demand for VPNs

Waves of new restrictions have directly correlated with surges in interest in VPN services. Users began actively searching for ways to bypass restrictions. Indirect evidence of rising demand has included intensified enforcement against VPN services: the national regulators restricted access to hundreds of circumvention tools, and dozens of VPN applications were removed from major app stores.
The world VPN market includes both international commercial VPN providers (such as NordVPN, Surfshark, ExpressVPN, and Proton VPN) and circumvention tools like Psiphon. Self-hosted solutions — which allow users to set up personal VPN servers (for example, via Amnezia) — occupy a distinct niche, as they are generally less vulnerable to the mass blocking of shared public IP addresses.
VPN providers most commonly rely on servers located in the United States, the United Kingdom, the Netherlands, Germany, France, Switzerland, Canada, the Nordic countries, Singapore, and Japan. These jurisdictions are typically chosen due to their developed infrastructure, connection quality, legal environment, and content availability.

Why VPN Growth Is Driving Demand for IP Addresses

The expansion of the VPN user base directly increases the need for large pools of public IP addresses. Each user effectively accesses the internet through a VPN provider’s IP address. When too many users share a single address, its reputation can quickly deteriorate: websites trigger captchas more frequently, financial institutions flag traffic as suspicious, and streaming platforms block overloaded IPs.
Another important factor is the continuous rotation of IP addresses in response to blocking measures. When government filters restrict known VPN subnets at scale, providers must expand their infrastructure, connect new address ranges, and distribute traffic across different data centres and autonomous systems. In this context, IP addresses become a consumable resource: some are blacklisted or lose their reputation over time, requiring constant replenishment of IP pools.

As the VPN audience grows, both server capacity and IP capacity must scale accordingly. In many cases, it is more efficient for providers to lease large IP blocks from hosting companies and address resellers than to rely solely on their own allocations. This effect becomes particularly visible during sudden spikes in demand — when a new wave of restrictions triggers mass VPN adoption, and services must rapidly increase the number of “clean” IP addresses to maintain performance and stability.

Conclusion

Widespread blocking and restrictions on internet services in various countries are fueling demand for VPN solutions. In turn, the expansion of the VPN market is increasing the need to lease and rotate substantial volumes of IP addresses. As a result, tighter internet controls are creating a chain reaction that affects not only end users but also the global IP address and infrastructure market.

What is new in Amazon Route 53’s IPv6 Support? You are doing it WRONG!

As a Customer Account Manager at InterLIR, I work daily with organizations navigating the complexities of IP address management and network infrastructure evolution. The recent announcement from Amazon Web Services regarding IPv6 support for Amazon Route 53 DNS service API endpoints represents a pivotal moment in cloud infrastructure development. This enhancement, introduced on November 21, 2025, addresses a critical need that many of our clients face: preparing their network infrastructure for the inevitable transition beyond IPv4 addressing limitations.

At InterLIR, we’ve witnessed firsthand the growing challenges organizations encounter as IPv4 address availability continues to decline. Since our founding in 2020 in Berlin, we’ve specialized in helping businesses navigate the IPv4 marketplace, but we also recognize that the future of internet infrastructure lies in IPv6 adoption. AWS’s implementation of dual-stack support for Route 53 represents exactly the kind of forward-thinking infrastructure development that organizations need to bridge the gap between today’s IPv4-dependent systems and tomorrow’s IPv6-native networks.

Understanding the Strategic Importance of DNS IPv6 Support

Domain Name System services represent the fundamental translation layer of the internet, converting human-readable domain names into machine-readable IP addresses. When we discuss DNS infrastructure with clients at InterLIR, we emphasize that DNS isn’t just a technical component-it’s a business-critical service that directly impacts application availability, user experience, and operational resilience.

The IPv4 addressing scheme, with its approximately 4.3 billion available addresses, served the internet well for decades. However, as our CEO Alexander Timokhin frequently points out in discussions about network availability, the exhaustion of IPv4 addresses has created significant challenges for organizations seeking to expand their digital infrastructure. The transition to IPv6, with its virtually unlimited addressing capacity of 2^128 addresses, isn’t merely a technical upgrade-it’s an essential evolution for sustainable internet growth.

Amazon Route 53’s implementation of dual-stack support at the route53.global.api.aws endpoint demonstrates a pragmatic approach to this transition. By supporting IPv6, IPv4, and dual-stack configurations simultaneously, AWS provides organizations with the flexibility to modernize their infrastructure at their own pace while maintaining operational continuity.

The Business Case for IPv6 Adoption

From my perspective working with diverse clients across industries, the business implications of IPv6 support extend far beyond technical specifications. Organizations face several converging pressures that make IPv6 adoption increasingly urgent:

Address Scarcity Economics – As IPv4 addresses become scarcer, their market value increases. Organizations that transition to IPv6 can reduce their dependence on expensive IPv4 address acquisitions

Regulatory Compliance – Government agencies and regulated industries increasingly mandate IPv6 compatibility, making it a compliance requirement rather than an optional enhancement

Competitive Positioning – Early IPv6 adopters gain advantages in serving global markets, particularly in regions where IPv6 adoption has accelerated

Operational Efficiency – Native IPv6 connectivity eliminates the overhead and complexity of address translation mechanisms

Future-Proofing – Organizations that implement IPv6 now avoid the technical debt and rushed migrations that late adopters will face

Dual-stack IPv4 and IPv6 network architecture diagram with routing infrastructure

Technical Implementation and Architecture Considerations

Working closely with our Head of Customer Support, Evgeny Sevastyanov, I’ve learned that successful infrastructure transitions require careful planning and clear understanding of technical implications. The Route 53 IPv6 implementation offers several architectural advantages that organizations should consider:

The dual-stack architecture maintains complete feature parity between IPv4 and IPv6 connectivity. This means that organizations can leverage Route 53’s full capabilities-including domain registration, DNS record management, traffic flow configuration, and health checks-regardless of which IP addressing scheme they use. This parity is crucial because it eliminates the risk of feature degradation during the transition period.

Route 53 Capability IPv4 Support IPv6 Support Business Impact
DNS Service API Endpoint Fully Supported Fully Supported Seamless connectivity regardless of addressing scheme
Domain Registration Available Available Unified management experience across IP versions
DNS Record Management Complete Complete Consistent operational procedures
Traffic Flow Configuration Enabled Enabled Global routing capabilities maintained
Health Checks and Monitoring Active Active Comprehensive visibility across both protocols

Backward Compatibility and Migration Pathways

One of the most significant aspects of AWS’s implementation is its commitment to backward compatibility. The existing IPv4-only endpoint remains fully operational, ensuring that legacy systems continue functioning without modification. This approach aligns with what we recommend to clients at InterLIR: never force disruptive changes when gradual transitions are possible.

Organizations can adopt several migration strategies depending on their specific circumstances:

Parallel Operation – Maintain both IPv4 and IPv6 connectivity simultaneously, allowing time for thorough testing and validation

Phased Rollout – Transition specific applications or services to IPv6 connectivity incrementally, reducing risk exposure

Geographic Segmentation – Implement IPv6 first in regions with higher adoption rates, expanding gradually to other markets

Service-Based Approach – Prioritize IPv6 implementation for new services while maintaining IPv4 for established systems

Industry Context and Market Dynamics

At InterLIR, our mission centers on solving network availability problems, and the IPv6 transition represents one of the most significant network availability challenges facing organizations today. Our Head of Sales, Alexei Krylov, regularly discusses with clients how IPv4 address scarcity impacts their expansion plans and operational costs.

Current industry data indicates that global IPv6 adoption reached approximately 41% by early 2025, but this figure masks significant regional variation. Some markets, particularly in Asia and parts of Europe, have achieved adoption rates exceeding 60%, while others lag considerably behind. This disparity creates both challenges and opportunities for organizations operating across multiple regions.

Several factors are accelerating the IPv6 transition:

Regional Internet Registry Policies – Most RIRs have exhausted their IPv4 address pools or implemented strict allocation policies, making new IPv4 acquisitions difficult and expensive

IoT Expansion – The proliferation of Internet of Things devices creates demand for billions of unique IP addresses, far exceeding IPv4 capacity

5G Network Deployment – Next-generation mobile networks are designed with IPv6 as the primary addressing scheme

Cloud-Native Architecture – Modern application architectures benefit from IPv6’s simplified networking model

Security Enhancements – IPv6’s built-in security features align with contemporary cybersecurity requirements

The IPv4 Marketplace Perspective

Working in the IPv4 marketplace gives me unique insight into how IPv6 adoption affects IPv4 address valuation and availability. While IPv6 represents the future, IPv4 addresses remain valuable assets for organizations that need to maintain compatibility with legacy systems or serve markets where IPv6 adoption remains limited.

The introduction of IPv6 support in critical infrastructure services like Route 53 actually validates the importance of dual-stack strategies. Organizations aren’t abandoning IPv4 overnight; instead, they’re building infrastructure that can operate effectively with both addressing schemes. This reality means that IPv4 addresses will retain value for the foreseeable future, even as IPv6 adoption accelerates.

Route 53 DNS architecture showing dual-stack IPv4 and IPv6 routing pathways

Practical Implementation Guidance for Organizations

Based on my experience helping clients navigate network infrastructure decisions, I recommend a structured approach to implementing Route 53’s IPv6 capabilities:

Assessment Phase

Begin by conducting a comprehensive assessment of your current DNS infrastructure and dependencies. Identify all applications, services, and systems that interact with Route 53, and evaluate their IPv6 readiness. This assessment should include:

  • Network infrastructure inventory and IPv6 capability verification
  • Application dependency mapping for DNS services
  • Security policy review and IPv6 considerations
  • Compliance requirement analysis
  • Cost-benefit evaluation of IPv6 implementation

Testing and Validation

Establish a testing environment that mirrors your production DNS configuration. Validate IPv6 connectivity to Route 53 endpoints and verify that all DNS operations function correctly. Key testing areas include:

  1. Basic connectivity verification to route53.global.api.aws via IPv6
  2. DNS record creation, modification, and deletion operations
  3. Health check functionality across both IP versions
  4. Traffic flow configuration and routing behavior
  5. Failover and redundancy mechanisms
  6. Performance benchmarking comparing IPv4 and IPv6 connectivity

Deployment Strategy

Implement IPv6 connectivity in a controlled, phased manner. Start with non-critical systems or development environments, gradually expanding to production workloads as confidence builds. Monitor performance metrics closely during the transition, paying particular attention to:

  • DNS query response times across both protocols
  • Error rates and connectivity issues
  • Traffic distribution between IPv4 and IPv6
  • Application behavior and user experience metrics
  • Security event patterns and anomalies

Cost Implications and Resource Planning

One of the most attractive aspects of Route 53’s IPv6 implementation is that AWS provides this enhancement at no additional cost across all Commercial Regions. This pricing approach removes a significant barrier to adoption and aligns with AWS’s strategy of encouraging infrastructure modernization.

However, organizations should consider the broader cost implications of IPv6 adoption:

Cost Category Considerations Potential Impact
Infrastructure Updates Network equipment IPv6 compatibility Variable based on existing infrastructure age
Training and Skills Development Staff education on IPv6 technologies Moderate investment in knowledge building
Testing and Validation Extended testing cycles for dual-stack operations Time and resource allocation for thorough validation
IPv4 Address Management Potential reduction in IPv4 address acquisition needs Long-term cost savings as IPv6 adoption increases
Operational Efficiency Simplified network architecture over time Gradual operational cost reduction

Security and Compliance Considerations

From a security perspective, IPv6 implementation requires careful attention to several areas that differ from traditional IPv4 security models. Organizations must ensure that security policies, firewall rules, and monitoring systems account for IPv6 traffic patterns.

Key security considerations include:

Firewall Configuration – Ensure that security groups and network ACLs properly handle IPv6 traffic

Monitoring and Logging – Extend security monitoring to capture IPv6-related events and anomalies

Access Control – Review and update access control policies to account for IPv6 addressing

Intrusion Detection – Verify that IDS/IPS systems can effectively analyze IPv6 traffic

Compliance Documentation – Update compliance documentation to reflect IPv6 implementation

Regulatory Requirements

Many organizations face regulatory mandates requiring IPv6 compatibility. Government agencies in the United States, European Union, and numerous other jurisdictions have established requirements for IPv6 support in new systems and services. These mandates affect not only government contractors but also organizations in regulated industries such as finance, healthcare, and telecommunications.

Route 53’s IPv6 support helps organizations meet these compliance requirements efficiently, providing a clear path to regulatory adherence while modernizing DNS infrastructure. For organizations operating in multiple jurisdictions, this capability simplifies compliance management by providing consistent IPv6 support across all AWS regions.

Future Outlook and Strategic Recommendations

Looking ahead from my vantage point at InterLIR, I see the Route 53 IPv6 enhancement as part of a broader transformation in internet infrastructure. The transition to IPv6 isn’t just about addressing capacity-it represents a fundamental shift in how we architect and operate network services.

Organizations should view this AWS enhancement as a catalyst for broader infrastructure modernization. The availability of IPv6 support in critical services like Route 53 removes technical barriers and provides a foundation for future-oriented network architecture.

Strategic Recommendations

Based on my experience working with organizations across various industries, I offer these strategic recommendations:

Begin Planning Now – Even if immediate IPv6 implementation isn’t urgent, start planning your transition strategy to avoid rushed decisions later

Adopt Dual-Stack Architecture – Implement systems that support both IPv4 and IPv6, providing maximum flexibility during the transition period

Invest in Skills Development – Ensure your technical teams understand IPv6 technologies and best practices

Monitor Industry Trends – Track IPv6 adoption rates in your industry and target markets to inform timing decisions

Evaluate IPv4 Asset Strategy – Consider how IPv6 adoption affects your IPv4 address holdings and whether optimization opportunities exist

Engage with Specialists – Work with experts who understand both IPv4 and IPv6 ecosystems to develop optimal strategies

Amazon’s implementation of IPv6 support for Route 53 DNS service API endpoints represents a significant milestone in cloud infrastructure evolution. As someone who works daily with organizations navigating the complexities of IP address management and network infrastructure, I view this enhancement as both a practical operational improvement and a strategic enabler for future growth.

At InterLIR, our mission focuses on solving network availability problems, and the IPv6 transition represents one of the most important network availability challenges facing organizations today. The Route 53 enhancement provides a clear, practical path forward-one that maintains backward compatibility while enabling modern addressing architecture.

The dual-stack approach AWS has implemented reflects the reality that IPv4 and IPv6 will coexist for years to come. Organizations don’t need to choose between the two; instead, they can build infrastructure that operates effectively with both addressing schemes. This flexibility is crucial for managing the transition without disrupting business operations.

For organizations considering their next steps, I recommend a measured approach: Begin testing IPv6 connectivity to Route 53 services in non-production environments. Validate that your applications and infrastructure can operate effectively with dual-stack configurations. Develop a phased implementation plan that aligns with your broader infrastructure modernization goals. And most importantly, view this transition not as a burden but as an opportunity to build more resilient, scalable, and future-proof network infrastructure.

The internet’s evolution toward IPv6 dominance is inevitable. Organizations that embrace this transition proactively, leveraging enhancements like Route 53’s IPv6 support, will be better positioned to navigate the changing landscape of internet infrastructure. Whether you’re managing DNS for a small application or orchestrating global traffic routing for enterprise systems, the availability of IPv6 support in Route 53 provides the foundation you need to build for tomorrow while maintaining operations today.

🌐 IPv4 Marketplace & LIR Services

GLOBAL IP ADDRESS SOLUTIONS

Professional broker services for secure IP transfers, reputation-clean address blocks, and LIR support across all regional registries.

Cookie Consent with Real Cookie Banner Privacy settings